Key Takeaway
- 📅 The record is fixed: the PhilHealth data breach started with the Medusa ransomware attack of September 22, 2023 — and the National Privacy Commission’s own count has since confirmed more than 42 million unique PhilHealth identification numbers in the leaked files.
- 🗂️ What got out: PhilHealth’s own public notice listed names, addresses, birth dates, sex, phone numbers, and PhilHealth identification numbers among the compromised data, while the NPC described the 734 GB dump as containing personal and sensitive personal information.
- 🔎 You can check yourself: the NPC runs a dedicated PhilHealth leak search tool — enter your 12-digit PIN and see whether it appears in the dataset the Medusa group released on October 5, 2023.
- ⚠️ The danger aged rather than faded: these records fuel the premium-refund and verification scam calls Filipinos still receive years later — because identity data does not expire, exposure does not either.
- ⚖️ The accountability file is open: the NPC launched a sua sponte investigation, DPA fines for grave offenses can reach 3% of annual income, and lawmakers confirmed in 2024 hearings that individual notifications had still not been sent.
Table of Contents
PhilHealth Data Breach: What Happened, Date by Date
The PhilHealth data breach is the incident that set the template every later Philippine government breach followed — an attack, a reassurance, a dump, and a regulator’s reckoning that kept growing for months. Here is the dated record, drawn from PhilHealth’s own statement, the National Privacy Commission’s findings, and the congressional testimony that followed.
September 22, 2023. PhilHealth’s urgent public notice states that on this date the Corporation suffered a cyberattack from the Medusa ransomware, which compromised data stored on some servers and local workstations. PhilHealth reported the incident to DICT, the NPC, the PNP cybercrime division, the CICC, and the NBI, and disconnected its network systems to contain the spread. The notice also asserted that the primary database was intact and not infected. Read the official notice yourself — it remains the primary document for the data types involved.
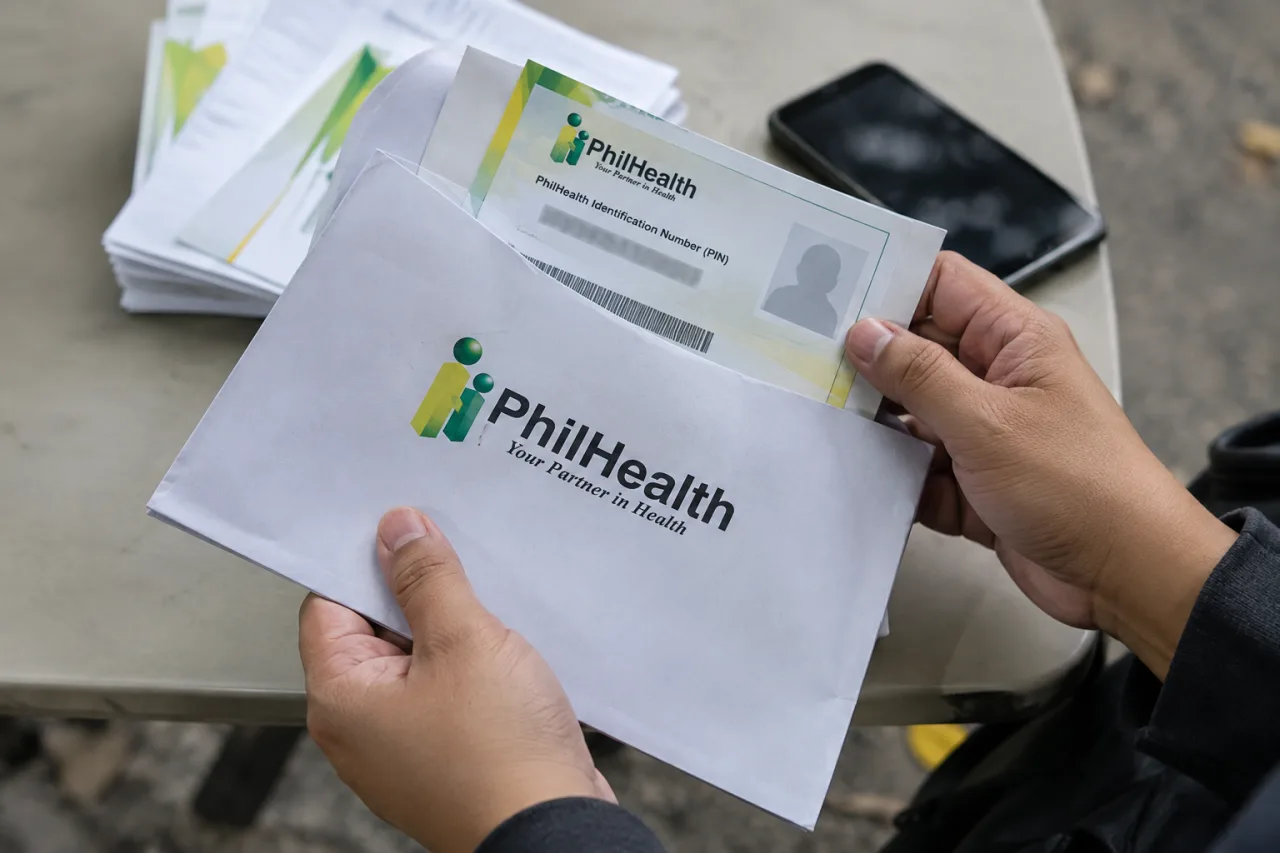
October 2-3, 2023. PhilHealth’s notice to the public listed what it believed had been compromised: names, addresses, dates of birth, sex, phone numbers, and PhilHealth identification numbers. It advised affected individuals to monitor for unauthorized activity, change passwords on financial accounts, and stay wary of follow-up contacts. The Record’s reporting preserved what PhilHealth claimed at that stage — that no personal and medical information had been compromised or leaked. The Record documented the shift that followed as the PhilHealth data breach moved from denial to confirmation: by October 2023 the government confirmed the records of 8.5 million senior citizens had been stolen in the attack.
October 5, 2023. Files purportedly released by the Medusa ransomware group appeared online — this is the dataset the NPC’s leak-checker tool references, and the National Privacy Commission announced its initial analysis of the 650 GB compressed dump, which extracted to around 734 GB of data containing personal and sensitive personal information. In response to the PhilHealth data breach dump, the NPC launched a sua sponte investigation into PhilHealth and its officials and warned the public that processing, downloading, or sharing the exfiltrated data is itself a punishable offense under the Data Privacy Act.
July 2024. At a House appropriations hearing, the NPC disclosed that the hackers had dumped 181 million records, with cleaning underway to deduplicate them. Insurance Business reported the figure that fixed the scale of the PhilHealth data breach: 42 million unique records — and the NPC’s leak-checker running count has since confirmed 42,089,693 PhilHealth identification numbers in the leaked database, a number that includes vulnerable groups — senior citizens, indigent members, and persons with disabilities. Lawmakers also heard the notification gap directly: PhilHealth’s executive vice president confirmed the organization had not provided notice to each victim as legally required, and representatives demanded the notification plan that law requires within days.
Multiple news outlets also reported a contributing failure that has aged into parable status: the antivirus software protecting PhilHealth systems had an expired license, meaning the very tool that should have flagged the intrusion was inert. Whether or not every detail of that account survives scrutiny, the lesson holds across every agency breach since — an expired defense is a closed defense.
What Was Actually in the Leaked Files
What the PhilHealth data breach actually exposed combines two sources: what PhilHealth listed in its own notice, and what the NPC confirmed after extraction.
Per PhilHealth’s October 2023 notice, the compromised data included, among other types: name, address, date of birth, sex, phone number, and PhilHealth identification number. Per the NPC’s analysis, the extracted dump contained personal and sensitive personal information — a category under the Data Privacy Act that covers health-related data and carries heightened protection. The confirmed volume grew from the 8.5 million senior-citizen records identified in October 2023 to the 42,089,693 unique identification numbers the NPC’s checker now counts. The commission stressed the dump did not represent the entire PhilHealth database of the era — the insurer held records on more than 103 million beneficiaries as of mid-2023 — which means a negative result in the checker does not certify your data was never touched.
What was not confirmed is equally worth stating plainly: PhilHealth maintained that its primary claims database stayed intact; the leaks centered on files and records pulled from servers and workstations; and no group has authenticated financial account details inside the PhilHealth data breach dump. The risk profile is identity-based — names, addresses, birthdays, phone numbers, and PINs matched together — which is precisely the identity kit that fuel-bombs verification scams. Our Philippine data leak 2026 roundup tracks how incidents of this class compound: individual agency breaches accumulate into a national exposure ledger of 155.6 million accounts.
Is Your PhilHealth Record in the Leak? How to Check
The regulator built the tool for this exact question. The NPC’s PhilHealth leak checker asks only for your 12-digit PhilHealth Identification Number and tells you whether it appears in the dataset the Medusa ransomware group purportedly released on October 5, 2023. The NPC emphasizes it does not collect or store what you type on that page, and the tool’s own scope note matters: it covers only that released dataset, not the entire leaked database or other breach incidents — so a clean result lowers the alarm, it does not clear the file.
Interpret the two outcomes accurately. A hit means your identity kit is definitively in criminal hands — treat every PhilHealth-branded call, text, or email as hostile until verified, and run the protective moves in the next section. A miss means your PIN was not among the confirmed 42 million — you still take the same hygiene, because the checker’s negative result is limited-scope by design. Our data breach checker guide covers the email-side checks that pair with the PIN check, and our piece on the data breach reporting channels shows where to file if the verification calls start.
What the Breach Means for Members Today
Years after the PhilHealth data breach, the practical exposure is the scam factory the records feed. Criminals holding name-plus-birthday-plus-phone kits run precise scripts: a call about your premium refund, a text about a suspended membership pending payment, an offer to fix your records for a fee, a link to a lookalike portal asking you to verify your PIN. An address that fails our Philippine government website is-real checks never sees your data at all. The data makes the scripts sound credible because they quote real details — that is the entire trick, and it does not decay with time.
The defense stack for members is short and boring, which is why it works. Treat any inbound contact claiming PhilHealth issues as a prompt to verify out-of-band: hang up and call the official hotline or visit the official portal directly, never through links sent to you. Never pay a fee to release, reactivate, or verify coverage — official transactions do not run that way. Change or de-duplicate passwords on portals where your PhilHealth credentials are reused; our 20-minute password vault build for government logins exists precisely because agency breaches keep proving the reuse math. And monitor financial accounts the way PhilHealth’s own notice advised — unfamiliar activity gets reported immediately to the bank’s fraud desk, not disputed by reply text.
One more member-side reality: contributions and claims continue, and the breach does not change how legitimate those processes run. Our PhilHealth claim guide for OFWs and the healthcare ransomware protection piece cover the service side and the hospital-side lessons, respectively — the breach does not suspend your benefits or your obligations, and scare texts claiming the opposite aim to rush you into paying a fake one.
The Investigation, the Law, and Where Things Stand
The accountability trail is the part of the PhilHealth data breach that is still live. The NPC’s sua sponte investigation — opened on its own initiative once the dump’s scale emerged — was tasked with ascertaining the full scope, identifying responsible officials, and pursuing prosecution to the extent the law allows. The Data Privacy Act’s penalty ladder gives those words weight: unauthorized processing and negligent breaches carry fines that can reach 3% of annual income, and negligence by personnel responsible for security carries criminal exposure. Congressional hearings in 2024 kept the pressure on the notification failures, asking PhilHealth for the status and plan of victim notifications as law requires.
For the public, the NPC’s warning deserves permanent quoting: anyone found to process, download, or share the exfiltrated data faces liability for unauthorized processing and potential criminal charges. Curiosity is not a defense. If a dataset linked to the PhilHealth data breach crosses your screen — as a recruiter, a researcher, or a bystander — the lawful move is to report it, not to open it.
The institutional lesson of the PhilHealth data breach fed directly into the reforms the country debates now: the proposed cybersecurity agency under HB 9605, the NPC’s doubled case load documented in our NPC incidents coverage, and the Data Privacy Act rights framework our rights guide explains — the tools members can actually use when an institution loses their records. The systemic picture — why these waves keep repeating and what the fixes cost — sits in our root-causes analysis of the hacks.
If You Are an OFW Member
Overseas members carry the same PhilHealth data breach exposure plus one complication: distance. Your PIN, your dependents’ data, and your payment history sat in the same systems, and scam texts now reach OFW numbers through the same leak kits. The extra moves for OFWs: treat any text about your PhilHealth contribution status from a Philippine number as verify-first — check through the official portal, not through the message; route family-side payments through official channels only, and our guide to paying SSS, PhilHealth, and Pag-IBIG from abroad lists those channels; and brief the family holding your dependent records on the same rules, because the calls will go to them too.
If the verification scam calls escalate into attempted fraud, the reporting channels are the same ones every Filipino uses — the NPC complaint route, the 1326 hotline, and the PNP Anti-Cybercrime Group, all covered step by step in our data breach reporting guide, including the routes for Filipinos filing from abroad.
FAQ
What happened in the PhilHealth data breach?
The Medusa ransomware attacked PhilHealth systems on September 22, 2023, compromising data on servers and workstations. Files purportedly released by the group appeared online on October 5, 2023. The NPC’s analysis extracted 734 GB of personal and sensitive personal information from the 650 GB compressed dump, and the running count on the NPC’s checker confirmed 42,089,693 unique PhilHealth identification numbers in the leaked database.
What data was leaked in the PhilHealth hack?
PhilHealth’s own notice listed names, addresses, dates of birth, sex, phone numbers, and PhilHealth identification numbers among the compromised types; the NPC described the dump as containing personal and sensitive personal information, with vulnerable groups — senior citizens, indigent members, and persons with disabilities — confirmed among the affected. No confirmed leak of financial account credentials was established.
How do I check if my PhilHealth data was in the leak?
Use the NPC’s PhilHealth leak checker at philhealthleak.privacy.gov.ph — enter your 12-digit PhilHealth Identification Number and the tool shows whether it appears in the dataset the Medusa group purportedly released on October 5, 2023. The NPC notes the tool does not store your input and covers only that released dataset, so a negative result is limited-scope, not a total all-clear.
Did PhilHealth have to notify affected members?
Yes — notification is the legal requirement, and congressional testimony in 2024 confirmed PhilHealth had not provided notice to each victim as required. Lawmakers demanded a notification status report and plan during the July 2024 hearings. Members were advised by PhilHealth’s own notice to monitor accounts, change passwords, and stay wary of follow-up contacts.
Is the PhilHealth leak still dangerous years later?
Yes — identity kits do not expire. Names, birth dates, phone numbers, and PINs remain usable for the verification and premium-refund scams that still target members today. The defense is behavioral: verify contacts out-of-band, never pay fees to release or reactivate coverage, and change reused passwords. Reports of fresh dumps or scam waves tied to the records keep the file active.
Who was held accountable for the PhilHealth data breach?
The NPC launched a sua sponte investigation to determine the full scope, identify responsible officials, and pursue prosecution under the Data Privacy Act, whose fines for grave offenses can reach 3% of annual income with criminal exposure for negligence. Congressional hearings continued into 2024 over the notification failures. Processing, downloading, or sharing the leaked data is itself punishable — the NPC has warned the public of that directly.
Financial Disclaimer
This article is published for general information only and does not constitute financial, legal, or investment advice. Event details, figures, and legal references reflect publicly available statements and reports at the time of writing and may change as investigations proceed. Readers should verify current guidance with PhilHealth and the National Privacy Commission, and consult qualified professionals for advice specific to their situation.
- Official philhealth.gov.ph/ofclstmnts/2023/UN2023-10-03.pdf — Read the official notice yourself
- therecord.media/philippine-lawmakers-want-answers-data-breach — documented the shift
- Official privacy.gov.ph/npc-takes-firm-stand-unwavering-commitment-to-protect-… — announced its initial analysis of the 650 GB compressed dump
- insurancebusinessmag.com/asia/news/cyber/philhealth-hack-potentially-…
- Official philhealthleak.privacy.gov.ph — PhilHealth leak checker
External sources linked in this article, in order of first mention. Spotted an error or a broken link? Tell us.
Cite this pagePublished Nov 10, 2026
Agron, E. (2026, November 10). PhilHealth Data Breach Explained: What Happened to Your Records. WorldNgayon. https://worldngayon.com/philhealth-data-breach/
Agron, Edmon. “PhilHealth Data Breach Explained: What Happened to Your Records.” WorldNgayon, 10 Nov. 2026, worldngayon.com/philhealth-data-breach/.
Agron, Edmon. “PhilHealth Data Breach Explained: What Happened to Your Records.” WorldNgayon, November 10, 2026. https://worldngayon.com/philhealth-data-breach/.
Agron, E. (2026) ‘PhilHealth Data Breach Explained: What Happened to Your Records’, WorldNgayon, 10 November. Available at: https://worldngayon.com/philhealth-data-breach/.
E. Agron, “PhilHealth Data Breach Explained: What Happened to Your Records,” WorldNgayon, Nov. 10, 2026. [Online]. Available: https://worldngayon.com/philhealth-data-breach/
@online{agron2026philhealthdata,
  author       = {Agron, Edmon},
  title        = {{PhilHealth Data Breach Explained: What Happened to Your Records}},
  year         = {2026},
  date         = {2026-11-10},
  organization = {WorldNgayon},
  url          = {https://worldngayon.com/philhealth-data-breach/},
  urldate      = {}
}TY - ELEC AU - Agron, Edmon TI - PhilHealth Data Breach Explained: What Happened to Your Records T2 - WorldNgayon PY - 2026 DA - 2026/11/10/ UR - https://worldngayon.com/philhealth-data-breach/ Y2 - ER -
Cite the version you read; the page may be updated. Zotero and Mendeley can also import this page directly.