The Flaw You Never See: Why 2026's Worst Breaches Ran Through IT Providers, Not Victims
Key Takeaway
🕳️ The msp breach is the flaw you never see — your IT provider’s, not yours: 2026’s ransomware record — 7,551 publicly disclosed victims in twelve months, up 24.9% — didn’t run through victims’ own mistakes; it increasingly ran through the trusted platforms that sit between businesses and their security, and the year’s biggest disclosure names the pattern.
🚨 The N-able N-central flaw is the year’s cleanest example: a critical pre-authentication remote-code-execution flaw (CVE-2026-86218, CVSS 10.0 — the maximum score) in the remote-monitoring software thousands of managed-service providers use to administer client endpoints — meaning ONE vulnerability, in one tool, touching every client that provider serves.
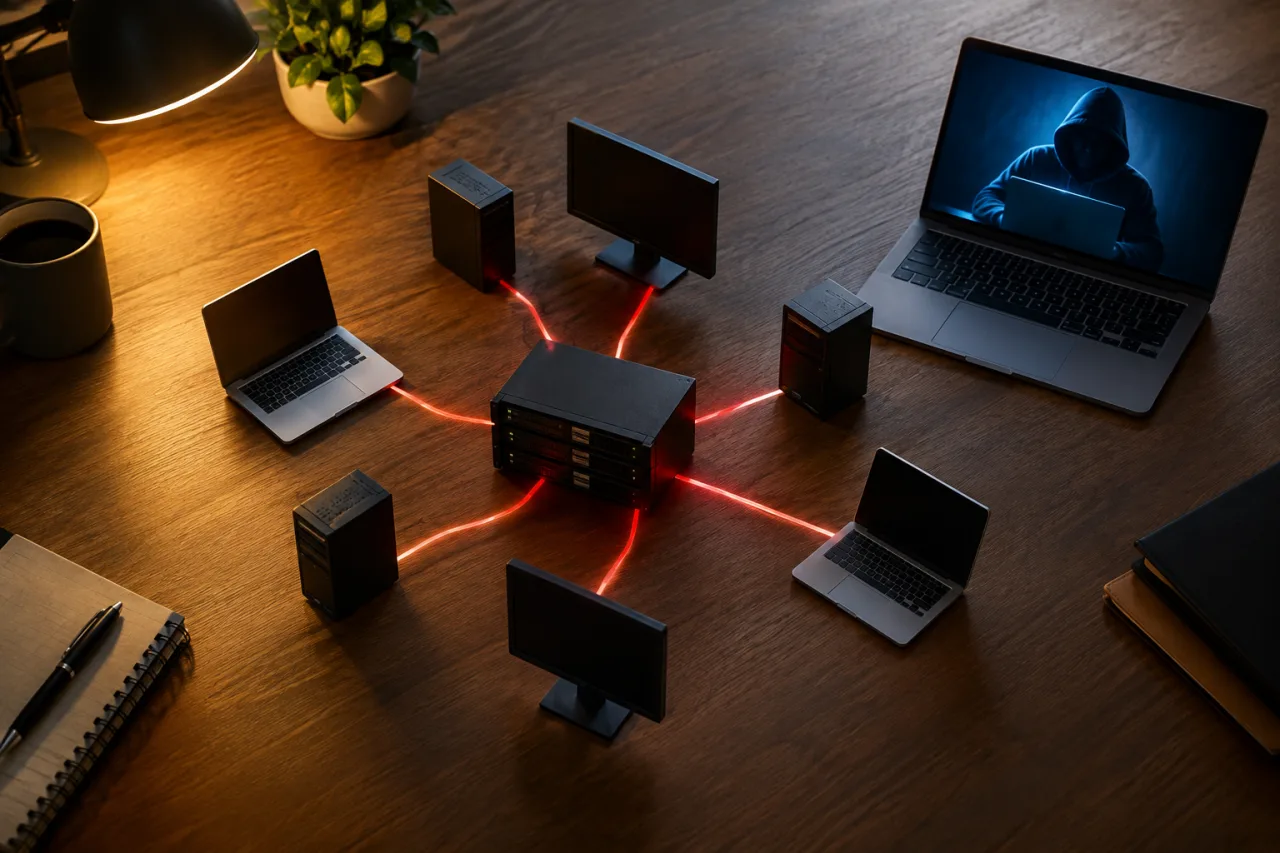
🧩 Delegated trust is the architecture that made this cheap: managed platforms hold standing access to hundreds of client networks by design — the Salesforce-OAuth abuse Black Kite’s 2026 report documents and the RMM flaw both exploit the same property: a breach you never touched, executed through software you never logged into, becomes YOUR breach.
❓ The three questions every small business should ask its provider now: which remote-management platform touches our network and at what access level; were this quarter’s critical flaws patched on YOUR side and when; and what does YOUR incident plan say about notifying us when the provider — not the client — is the breach.
🛡️ The practical defense is a two-layer check: the client-side hardening that limits standing access (MFA on the provider’s own login, least-privilege scoping) plus the vendor side that matters most: a provider who patches fast, discloses fast, and rehearses the msp breach scenario — the same readiness doctrine the ransomware playbooks preach, pointed at the door you didn’t know you had.
Table of Contents
The msp breach is the attack that runs through the company you hired to keep you safe, and 2026 made it the ransomware year’s main character: 7,551 publicly disclosed victims between April 2025 and March 2026 — a fourth straight record — with the trusted-vendor platforms designated the year’s primary attack path. The N-able N-central disclosure put a face on it: a maximum-severity pre-auth flaw in the remote-monitoring software that manages other people’s networks for a living. This explainer covers what an RMM tool is and why its compromise outranks yours, the provider-chain architecture that turned a few vendor breaches into a thousand-client problem, the questions that separate a hardened provider from a breach relay, and the client-side moves that shrink your exposure to flaws you cannot patch and never see — the security conversation 2026 forced onto every small business that thought its own servers were the boundary.
The MSP Breach Problem: What an RMM Tool Is and Why Its Flaws Outrank Yours
Managed-service providers (the IT firms small businesses rent instead of hiring) run their client networks through remote monitoring and management platforms — software with one job: total standing access to hundreds of endpoints at once. The N-able N-central disclosure that hit this season describes the worst-case flaw in exactly that class: a critical pre-authentication remote-code-execution vulnerability (CVE-2026-86218, CVSS 10.0) — reachable without logging in, executing on the server that itself holds your credentials, your endpoint registry, and the management tunnel. A 10.0 flaw in a desktop app is an annoying patch; an msp breach in the same score class the same flaw in an RMM is a master-key problem, because the attacker who takes the provider’s platform inherits every client the provider manages — the math that turns one unpatched vendor into a multi-business ransomware morning. The provider chain is not a hypothetical: the remote-management lane has produced exactly this pattern before, and the score that names the class — maximum severity, pre-auth — is the tell to watch in every vendor advisory that arrives during the year.
The Delegated-Trust Architecture: Why One Breach Ripples a Thousand Ways
The structural problem Black Kite’s 2026 report names plainly: of 7,551 disclosed victims in the reporting year — a 24.9% rise — the trusted-vendor platforms became the primary attack path, with Salesforce OAuth abuse documented as the delegated-trust case study. The architecture works because it’s convenient: OAuth grants, RMM tunnels, and SaaS integrations give third-party platforms standing access to business systems, trading a patch-and-vigilance burden for an operational one. The trade’s hidden price shows on the vendor’s worst day — the client who “did everything right” inherits the breach through the connection the client never configured. The report’s own framing is the practical lesson: a company can be fully patched, well-trained, and still extorted over an infrastructure it never touched — the year’s records were set by attackers who understood that breaking one well-connected vendor beats phishing a hundred well-trained customers.
The Client’s Questions: How to Vet a Provider’s Security, Concretely
The vetting conversation that prevents every preventable msp breach small businesses should hold now — and the questions the MSP-management guides structure around — runs on three axes. Access: “which remote platforms reach my endpoints, with what privilege, and can the standing access be scoped down to task-by-task?” Operations: “when were the quarter’s critical vendor advisories (including your own tooling’s) patched on platforms that manage me — and do you run the disclosure standard that tells clients before rumors do?” Readiness: “if YOU are breached, what do I get — a same-day notice, an evidence timeline, and a remediation plan?” The answers grade the provider; the evasions grade harder. What the answers CANNOT fix: a provider who doesn’t run the provider-is-the-breach rehearsal — the year’s reporting keeps the playbook point: a strategy drafted on a calm day is the difference between a contained incident and an untrained scramble, and the scramble is what actually kills small operations.
The Client-Side Defense: Shrinking Standing Access You Can’t Patch
Four client-side moves cut the msp breach exposure that stands in delegated access meaningfully, and none requires the provider to change anything. MFA on the provider’s own customer portal (the account-takeover lane into the RMM dies at the portal). Least-privilege scoping: the provider’s agent doesn’t need domain-wide rights to run patches and alerts — the scoping conversation is the vetting conversation’s concrete half. The monitoring layer: log the RMM’s own connections — the tool that touches every endpoint leaves the same trail every other insider does, and the trail answers the “was it them or us” question at incident time. And the fallback: a tested local recovery path (offline backups, a second admin identity, an out-of-band communication plan) so that a provider outage — breach, flaw, or bankruptcy — is an inconvenience rather than a blackout. The incident-response guide runs the rehearsal logic in full; the provider outage is scenario number one the rehearsal should include.
The Market Direction: Vendors Who Patch Fast Are the Product
The vendor-selection criteria this wave makes decisive: patch velocity and disclosure honesty outrank feature sheets. The RMM vendors who shipped emergency fixes on the N-central-class disclosures and published timelines earn the retention; the ones who let quarters lapse on 10.0-class flaws earn the exit. For the small business, the market signal is legible without a security team: vendor advisories that arrive WITH patch guidance same-week, breach disclosures that name affected platforms rather than wait for journalists, and provider contracts that name the notification windows in writing. The threat-actor side of Black Kite’s ledger — 127 active groups through the reporting close, 146 by June 2026, with the volume market growing at the bottom while concentrating at the top — is the reason this is no longer optional diligence: the buyers of RMM access are professionalized, priced, and shopping; the sellers are the vendors, and the small business is the inventory.
The MSP Breach Readiness Checklist: the Two-Layer Setup
The two-layer setup turns vetting into a standing state. The client layer, this quarter: MFA on every vendor portal that can reach your systems, the access-scoping review (what does the provider’s agent actually run as), the log destination for RMM connections confirmed, and the offline-backup restore tested once — the restore test being the layer every guide in this series ranks first because it answers every breach scenario, provider-caused or not. The vendor layer, this quarter: the three vetting questions asked in writing (platform and versions; the quarter’s critical advisories patched, with dates; the incident-notice commitment to clients), the provider’s disclosure history checked (advisory pages, patch timelines — the vendors who publish earn the standing trust), and the contract’s breach-notice clause read once more than feels necessary. The msp breach layers take an afternoon together, and the afternoon buys the only security property that survives the year’s attack path: proof — in logs, contracts, and tests — rather than trust. The ransomware market that grew around delegated access prices its targets by exactly the absence of that proof; the checklist is the small business declining to be the inventory.
Frequently Asked Questions
What Is an MSP RMM Vulnerability and Why Does It Affect Me?
An RMM (remote monitoring and management) tool is the software your IT provider uses to manage your computers and servers — and its vulnerabilities matter because the tool holds standing access to everything it manages. A critical flaw like N-able N-central’s pre-auth RCE (CVSS 10.0) means an attacker can reach the provider’s platform without credentials; from there the compromise inherits YOUR network through the management tunnel. If a provider manages your systems, their tooling’s security IS your security — the flaw you never see, one patch away from being yours.
How Do I Check if My Business Uses N-able or Another MSP Platform?
Ask your provider directly, in writing: “which remote-management software do you use to administer our endpoints?” The answer is one of a handful of products (N-central, the ConnectWise family, Datto, Syncro, and peers) — and the reply itself is a test: a provider who answers in a day with the version and patch status is doing the diligence you’re asking for. The follow-up question: “was the platform patched for the current quarter’s critical advisories, and when?”
Am I Liable if My Data Is Breached Through the IT Provider’s MSP Platform?
The data is yours, so the notification obligations, regulator contact, and customer-facing fallout generally follow you — the provider’s contractual and (sometimes) insurance obligations run in parallel, and the contract’s language decides much of it. The practical checklist: review the provider agreement’s breach-notice and indemnity clauses before the incident, not the morning after; the cyber-insurance question runs separately — the coverage that pays your breach response exists, and the provider’s own policy covers the provider. The incident-response guide’s rehearsal covers both halves.
What Should I Ask My MSP After the N-Central Disclosure?
Three questions, in writing: which N-central (or other RMM) version manages our endpoints; was CVE-2026-86218 — the maximum-severity pre-auth flaw — patched on the platform that touches us, and when; and what does your own incident plan say about notifying clients when your infrastructure is the breach. A provider who answers all three unprompted is demonstrating the patch-velocity standard; the one who answers none of them is telling you where your real risk sits.
How Can a Small Business Protect Itself From a Vendor MSP Breach?
Four layers, all client-side: MFA on the vendor’s own portals, least-privilege scoping of every third-party agent and integration, monitoring of the platform’s connections plus the local logs that answer the attribution question at incident time, and the tested offline-recovery path that survives a provider outage of any cause. None requires the vendor’s cooperation; together they shrink “the flaw you never see” into a survivable event — which is the whole standard the year’s ransomware record demands of every small operation.
Financial Disclaimer
This article provides general security-information guidance and does not constitute legal, financial, or professional advice. Vulnerability disclosures, patch status, and insurance terms change over time; verify against official vendor advisories and CISA alerts before acting. The author and publisher disclaim any liability for actions taken based on this information.
External sources linked in this article, in order of first mention. Spotted an error or a broken link? Tell us.
Cite this pagePublished Nov 2, 2026
APA 7
Agron, E. (2026, November 2). Your MSP Got Hacked: the N-able 10.0 Flaw and the Vendor-Trust Problem Behind 2026’s Ransomware Record. WorldNgayon. https://worldngayon.com/msp-breach/
MLA 9
Agron, Edmon. “Your MSP Got Hacked: the N-able 10.0 Flaw and the Vendor-Trust Problem Behind 2026’s Ransomware Record.” WorldNgayon, 2 Nov. 2026, worldngayon.com/msp-breach/.
Chicago
Agron, Edmon. “Your MSP Got Hacked: the N-able 10.0 Flaw and the Vendor-Trust Problem Behind 2026’s Ransomware Record.” WorldNgayon, November 2, 2026. https://worldngayon.com/msp-breach/.
Harvard
Agron, E. (2026) ‘Your MSP Got Hacked: the N-able 10.0 Flaw and the Vendor-Trust Problem Behind 2026’s Ransomware Record’, WorldNgayon, 2 November. Available at: https://worldngayon.com/msp-breach/.
IEEE
E. Agron, “Your MSP Got Hacked: the N-able 10.0 Flaw and the Vendor-Trust Problem Behind 2026’s Ransomware Record,” WorldNgayon, Nov. 2, 2026. [Online]. Available: https://worldngayon.com/msp-breach/
BibTeX
@online{agron2026mspbreach,
  author       = {Agron, Edmon},
  title        = {{Your MSP Got Hacked: the N-able 10.0 Flaw and the Vendor-Trust Problem Behind 2026’s Ransomware Record}},
  year         = {2026},
  date         = {2026-11-02},
  organization = {WorldNgayon},
  url          = {https://worldngayon.com/msp-breach/},
  urldate      = {}
}
RIS
TY  - ELEC
AU  - Agron, Edmon
TI  - Your MSP Got Hacked: the N-able 10.0 Flaw and the Vendor-Trust Problem Behind 2026’s Ransomware Record
T2  - WorldNgayon
PY  - 2026
DA  - 2026/11/02/
UR  - https://worldngayon.com/msp-breach/
Y2  -
ER  -
Cite the version you read; the page may be updated. Zotero and Mendeley can also import this page directly.