Table of Contents
Key Takeaway
- 📲 The authenticator app wins the comparison the attack actually experiences: an SMS code rides the phone network, where SIM swaps, port-out tricks and SS7 interception operate, while an authenticator app keeps its secret on your device and generates its code there.
- ⚖️ NIST ranks them in writing: the federal standard classifies SMS out-of-band codes as a restricted authenticator, while authenticator-app TOTP remains fully acceptable as a second factor when paired with a password.
- 🕵️ Neither method stops a real-time phishing page: both hand you a code you type somewhere, and a convincing fake site can relay it, so treat every app-or-SMS comparison as a step up, not a finish line.
- 🏦 Your bank decides your timeline: if the app or online-banking settings offer authenticator enrollment, switch on a quiet weekend; if SMS is the only second factor offered, lock the SIM and watch for in-app prompts that could take its place.
- 🔑 The switch fails when codes get lost, not when codes get stolen: enroll the QR, save the backup codes somewhere that is not the phone, and run one test login before you drop SMS.
Both factors produce the same six numbers and type into the same box, which is why the argument sounds like a coin flip. It is not. The difference is where the secret lives: SMS verification sends a code through the telephone network to whatever device controls your number, and an authenticator app computes its code on your own device from a secret enrolled once. Every attack that distinguishes the two flows from that single line, and every reason to move to the authenticator app. An authenticator app also scales across every account you own: one app holds the codes for banking, wallets and email alike.
Authenticator App vs SMS: the Difference the Attack Sees
An SMS second factor trusts the telephone system as a secure courier. The service generates a code, hands it to the carriers, and assumes only your phone receives it. Attackers have spent a decade proving that assumption optional: SIM swap fraud convinces a carrier to move your number onto another SIM, after which every incoming code belongs to the thief; number porting reroutes the same way through retail processes; and SS7 interception reads codes from the signaling layer without your phone so much as buzzing. NIST catalogs these weaknesses by name in its authentication guidance and classifies SMS out-of-band codes as the one authenticator type marked restricted in its framework.
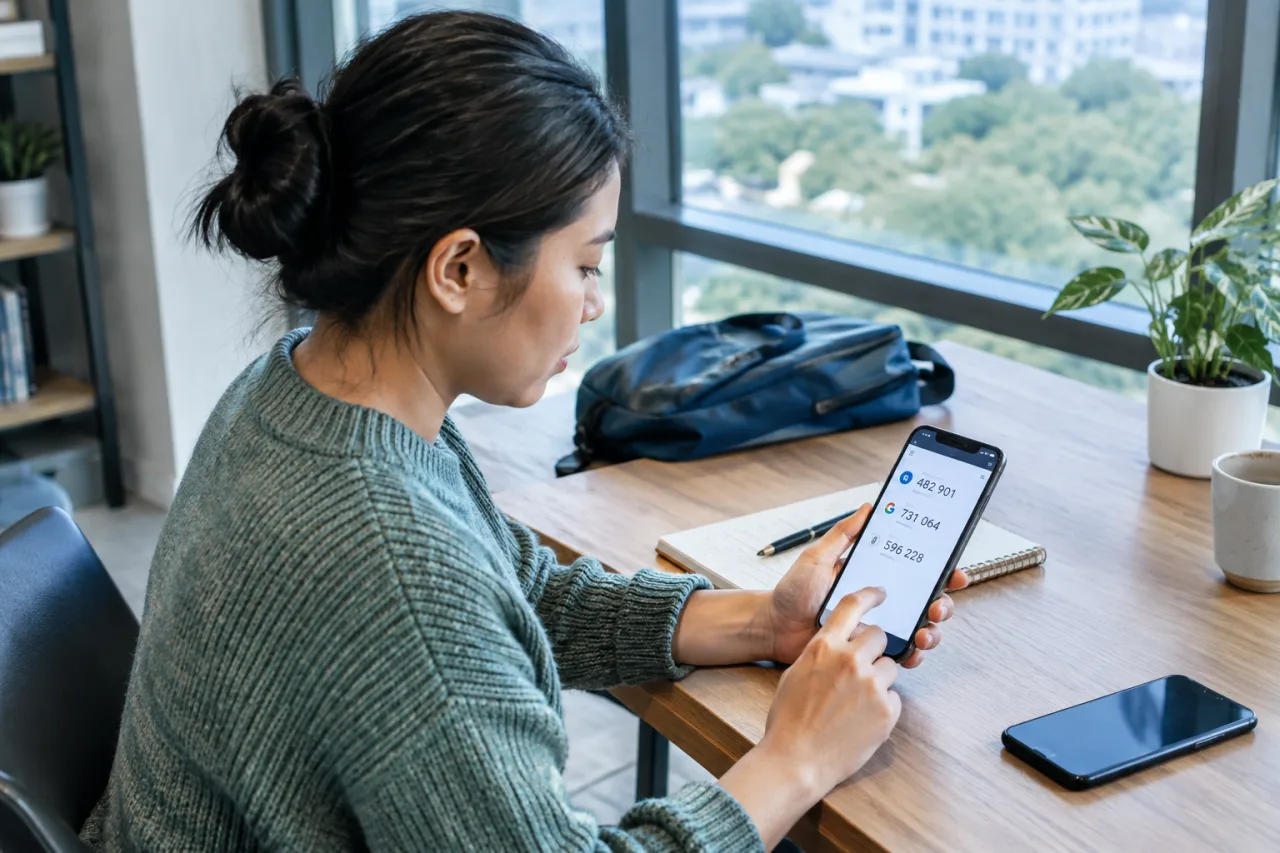
An authenticator app works the other way around: at enrollment you scan a QR code once, the secret never travels by phone network again, and each code is computed locally on a 30-second clock. Nothing arrives to intercept. To get a valid code, an attacker needs the device that holds the secret, malware that can read it, or a lookalike login page that tricks you into reading the code aloud — a narrower set of problems, and the reason the security community treats app-based verification as the working upgrade.
The real limitation belongs in the same paragraph, because you will meet it in your own setup guides: both methods end with a code you type by hand, and a polished phishing page can capture and relay either one in real time. NIST says so explicitly. The method that ends hand-typed codes entirely is the passkey, which binds the login to the site itself; our passkey setup guide covers that endpoint where the banks and wallets support it.
Why the Timeline Is Getting Urgent Either Way
The market is forcing the move. Microsoft has told its users that SMS-based verification ends for Microsoft accounts in February 2027, which our guide to the SMS shutdown covers in full, and enterprise security guidance across the industry points the same direction: treat app codes as the interim target and passkeys as the destination. For a reader in Riyadh or Manila, the practical reading is simple: any account that still uses SMS verification will ask you to move inside the next year or two, and the authenticator app enrollment you do tonight is the migration already banked, and the quiet weekend you spend switching now is the one that never becomes an emergency weekend later.
The other force is volume. Account-takeover operations buy and recycle phone numbers across whole regions, and the same operations have learned to trigger carrier port-outs by phone. When the second factor is only a phone number, your security and your carrier’s customer-service training are the same wall.
How to Check What Your Bank and Wallet Actually Offer
Do not assume the menu. Open the security or verification settings inside your banking or wallet app and look for four things in order: an option called authenticator, two-factor authentication, TOTP or Google Authenticator enrollment that displays a QR code; a prompt asking you to install or scan with an authenticator app; a downloadable backup-code page; and finally the SMS toggle you are trying to migrate away from. If the menu names an authenticator app, enrolment takes one scan. Banks that support app-based verification almost always describe it in exactly those words, because the QR-and-secret flow is a standard. If the security menu offers only SMS codes and nothing else, you have your answer for that account until the bank ships an update, and the SIM lock below becomes the working substitute until an authenticator app lands in that bank’s settings.
Where you see the QR flow, that account is ready for migration the same evening. Where you see in-app verification prompts instead — some major wallets have moved code delivery inside the app itself — the app-versus-SMS question dissolves, because the prompt is already bound to the device holding the session; our GCash OTP guide walks that wallet pattern. And where only SMS exists, note it beside an account you will revisit, because NIST’s restricted classification is quietly reshaping bank backends and the option appears with updates. Run the check in one sitting across the three account groups that matter most. For the email accounts first, because every other password reset lands there; for the bank and wallet apps, because the money lives there; and for the shopping and subscription accounts last, because the damage there is bounded. Note the result beside each account and the whole migration plan writes itself.
The check also tells you how fast each institution is moving. Institutions that shipped authenticator enrollment, backup codes and clear migration notes are executing the same standards the regulators describe. Institutions still SMS-only are the ones to watch, and their security pages are worth a revisit after their next major app update.
The No-Lockout Migration Path, Step by Step
Lost codes are the real reason people abandon the switch, and the path around it is a written sequence, not a leap of faith. The sequence exists because the failure mode is specific: an account enrolled to a secret that lives in only one place, a phone that breaks, and no second copy anywhere. Keep SMS enabled while you enroll. In the account’s security settings, choose the authenticator option, scan the displayed QR with the app, and confirm by typing the first code it generates. Next, find the backup or recovery codes page the enrollment usually links to, and save those codes somewhere that is not the phone: printed and filed, or in a manager that backs up separately. The etiquette is simple: treat backup codes like spare house keys, never photograph them into the camera roll, never email them to yourself, and never paste them into a chat where they will live forever. Then, and only then, run one full login with the authenticator code on a different device or after closing the app, so you have proof the pairing works. Only after the test passes do you turn the SMS option off, and even then leave the SIM protected in case the bank still texts about transactions. The test is the step users skip at their peril: it catches a mistyped QR, a wrong clock on the phone and a mispaired account while the SMS option still exists as the safety net. One test login per account, run while both factors are live, is the whole insurance policy.
The same sequence survives a phone upgrade without anxiety, which is the second disaster people fear. Before migrating devices, confirm the app supports cloud backup or multi-device secret export, re-enroll the accounts from the new phone while the old one still runs, and only after the new phone generates valid codes does the old phone lose status. And if you are the person a whole family depends on, the desktop route exists for exactly this: a separate device can hold the same authenticator app codes, which our Google Authenticator on Windows guide explains with the real options.
When SMS Is All You Have
Some accounts will not offer an authenticator option for years, and the answer there is hardening rather than surrender. Put a port-out PIN or SIM lock on the carrier account, the small setting that converts the easiest SIM-swap story into a long argument. Ask the bank whether in-app verification exists as an alternative and check the security menu again after major app updates. And read every incoming text with the assumption the network can leak it: forward the ones that arrive from strangers to 7726, report them to the carrier, and a code that arrives without you requesting one means an attacker already has your password, so the code goes in the bin and the password changes in the app, not through any link or caller.
Between the carrier lock and the in-app prompts the banks are shipping, an SMS-only account is no longer defenseless the way it was in 2019. It is a waiting room. The accounts you can move today, move; the accounts you cannot, lock down and watch.
FAQ
Is an authenticator app safer than SMS verification?
Yes, on the delivery channel that matters. The app computes codes on your device from an enrolled secret, so SIM swaps, port-outs and network interception stop mattering, and NIST classifies SMS codes as a restricted authenticator while app-based verification stays fully acceptable. Both still end in a typed code, so neither finishes the phishing problem. The ranking also explains what to ask for: when a bank offers app enrollment, the question about SMS safety has already been answered at the standards level, and you are choosing whether to take the upgrade the institution shipped.
Why did NIST classify SMS codes as restricted?
Because the telephone network is the trusted courier for the code, and its weaknesses are cataloged: SIM reassignment through social engineering, number porting and SS7 interception. Restricted means the method needs conditions — an alternative offered, users warned, risk assessed and a migration plan — not that every SMS login is forbidden.
What is a SIM swap, in plain terms?
An attacker convinces a carrier or retailer that they are you, moves your phone number to a SIM in their possession, and every text meant for you arrives on their phone instead — including verification codes. A carrier port-out PIN is the cheapest counter, and an authenticator app is the move that takes the code out of that fight entirely.
Can a phishing site steal an authenticator code?
It can, if it tricks you fast enough, because an authenticator code is six numbers you can read to anyone. That is the shared weakness of app and SMS codes, and it is why security standards point to passkeys as the endpoint: passkeys cannot be read out, since nothing travels for a fake site to capture.
What happens if I lose my phone with the authenticator on it?
The enrolled secret dies with the device, which is why migration exists as a written sequence: save the backup codes off-device at enrollment, confirm multi-device or cloud-backup support in the app before you depend on it, and re-enroll accounts on a new phone while the old one still runs. The families who lose access are the ones who skipped the backup-code page. The same written sequence is what any bank counter staff hand over when a customer asks, translated for the branch window. Bringing the question to the bank is how the whole switch becomes routine instead of exceptional, and the household that asks together finishes together.
What is TOTP, in plain terms?
Time-based one-time password: the standard the authenticator apps implement. The service shows a QR code at enrollment, the app stores the secret it encodes, and both sides compute a fresh code from the same clock, which is why the app works with no signal at all. The standard is public and old enough to be everywhere, which is why nearly every authenticator app interchanges with nearly every service.
Which apps work as an authenticator?
Google Authenticator, Microsoft Authenticator and similar TOTP apps all implement the same standard, and many password managers generate the same codes. The standard is what matters: any authenticator app that scans the QR and produces the 30-second codes works with any account that offers authenticator enrollment, though backup and export features differ between apps and deserve a check before you choose one.
- Official pages.nist.gov/800-63-3-Implementation-Resources/63B/Authenticators — authentication guidance
- Official pages.nist.gov/800-63-3/sp800-63b.html — marked restricted
External sources linked in this article, in order of first mention. Spotted an error or a broken link? Tell us.
Cite this pagePublished Nov 21, 2026
Agron, E. (2026, November 21). Authenticator App vs SMS: Which 2FA Is Actually Safer. WorldNgayon. https://worldngayon.com/authenticator-app-vs-sms/
Agron, Edmon. “Authenticator App vs SMS: Which 2FA Is Actually Safer.” WorldNgayon, 21 Nov. 2026, worldngayon.com/authenticator-app-vs-sms/.
Agron, Edmon. “Authenticator App vs SMS: Which 2FA Is Actually Safer.” WorldNgayon, November 21, 2026. https://worldngayon.com/authenticator-app-vs-sms/.
Agron, E. (2026) ‘Authenticator App vs SMS: Which 2FA Is Actually Safer’, WorldNgayon, 21 November. Available at: https://worldngayon.com/authenticator-app-vs-sms/.
E. Agron, “Authenticator App vs SMS: Which 2FA Is Actually Safer,” WorldNgayon, Nov. 21, 2026. [Online]. Available: https://worldngayon.com/authenticator-app-vs-sms/
@online{agron2026authenticatorapp,
  author       = {Agron, Edmon},
  title        = {{Authenticator App vs SMS: Which 2FA Is Actually Safer}},
  year         = {2026},
  date         = {2026-11-21},
  organization = {WorldNgayon},
  url          = {https://worldngayon.com/authenticator-app-vs-sms/},
  urldate      = {}
}TY - ELEC AU - Agron, Edmon TI - Authenticator App vs SMS: Which 2FA Is Actually Safer T2 - WorldNgayon PY - 2026 DA - 2026/11/21/ UR - https://worldngayon.com/authenticator-app-vs-sms/ Y2 - ER -
Cite the version you read; the page may be updated. Zotero and Mendeley can also import this page directly.