Key Takeaway
- 🛡️ What Claude Code Security is: Anthropic’s AI-powered vulnerability scanner, built into the Claude Code developer platform and launched February 20, 2026 in limited research preview — it reads entire codebases, reasons about how the pieces interact, and recommends precise fixes, rather than pattern-matching signatures like classic static analyzers.
- 📉 The selloff case study, dated: the launch wiped more than $15 billion from cybersecurity stocks within hours — the market repriced the portion of security workflows (continuous monitoring, triage, remediation drafting) that an AI system can now perform end-to-end.
- 🧠 Why the market reacted so hard: security software sells continuous vigilance; an AI tool that scans, understands AND drafts remediations compresses the very line items the sector’s revenue rests on — investors treated the February 20 launch as evidence the compression had started, and the repricing ran ahead of the product’s actual capabilities.
- 🧪 The honest limits: the tool shipped as a research preview; AI security findings still require engineering review (false positives, business-logic blind spots, and the “the AI missed it” failure mode are all live); and the practical workflow it created is AI-drafts-the-fix, human-owns-the-merge.
- 🧭 The operator takeaways: treat AI security scanners as force multippliers for your engineers (not their replacements), review every AI-proposed fix with the same rigor as code review, and watch the market signal — the February Claude Code Security selloff was the sector’s clearest statement yet that AI-native security is now priced as competition.
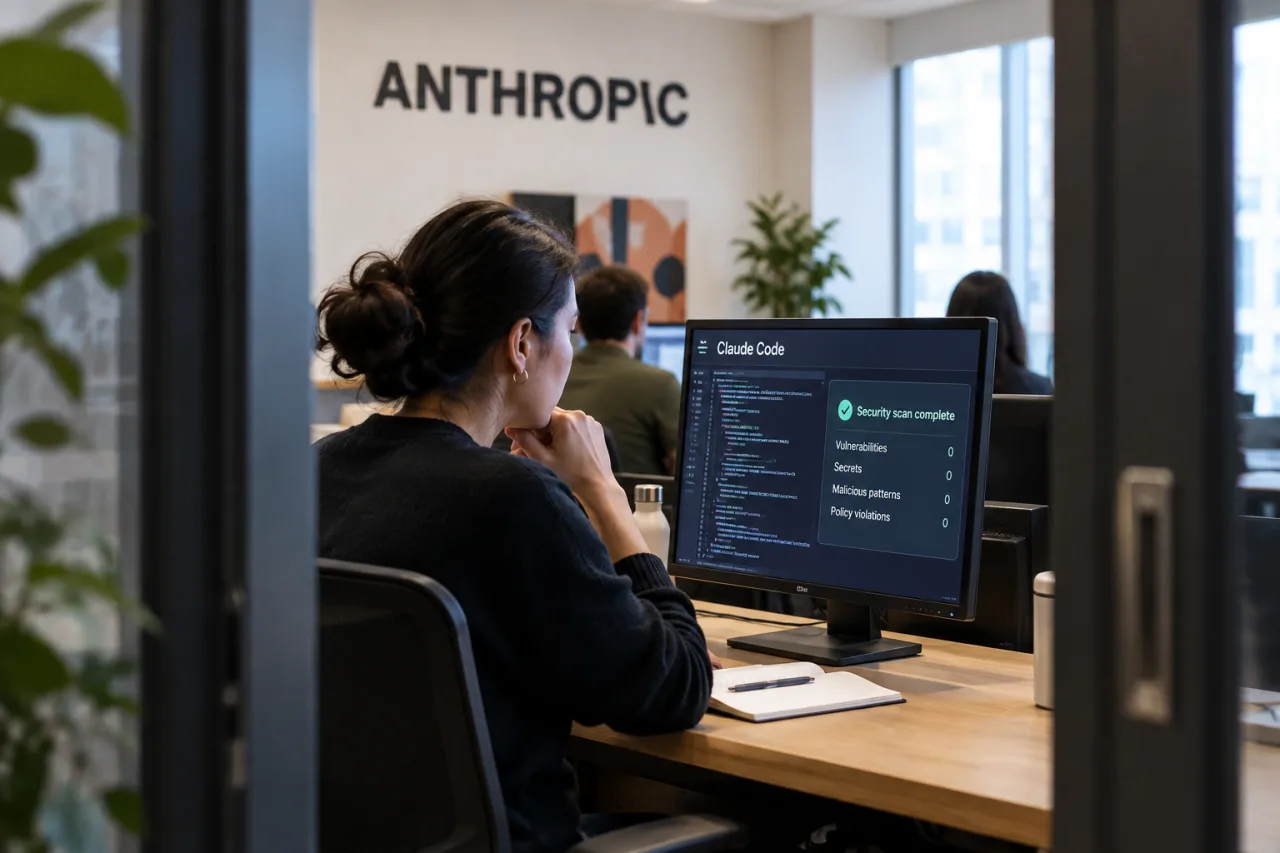
Claude Code Security is the AI security tool that moved markets before it shipped to everyone. On February 20, 2026, Anthropic launched Claude Code Security — an AI-powered vulnerability scanner built into its Claude Code developer platform, released first as a limited research preview. According to the company, the system represents a shift from traditional static analysis toward AI-driven reasoning: it scans software codebases for vulnerabilities, understands how components interact, and drafts precise fixes — the work traditionally split between human security engineers and specialized enterprise scanners. The market’s verdict arrived within hours: more than $15 billion was wiped from cybersecurity stocks as investors repriced the workflows the tool touches. This guide explains what the tool does, why the selloff ran as hard as it did, how AI scanning differs from signature analysis, and the workflow that makes the tool safe to use in real codebases.
Table of Contents
What Claude Code Security launched
The product, as launched February 20, 2026: a vulnerability-scanning capability embedded in Claude Code — Anthropic’s coding-agent platform — released in limited research preview. Where classic static application security testing (SAST) pattern-matches known-dangerous code shapes against rule databases, Claude Code Security reads the codebase the way a reasoning model reads anything: in context. The difference is operational, not cosmetic — a classic scanner flags lines; a reasoning scanner evaluates flows. Per Anthropic’s framing, the tool marks the shift from static analysis systems toward AI-driven reasoning systems for security review.
What that means in practice for a development team: the scanner can evaluate a proposed change in the context of the surrounding system — how a new authentication path interacts with the existing token flow, whether a “fixed” injection risk was fixed completely, whether the fix itself introduces a new exposure — and draft the remediation as code a reviewer can inspect. That last capability is the one the market feared most: fixing, not just finding, is where the enterprise-security workflow’s billable hours live.
WorldNgayon Analysis: the launch is best read as the security layer’s SaaS-crisis moment in miniature — the same repricing logic this site traced across the AI economy (the bubble ledger, the crash-question discipline): when a capability generalizes, the market reprices the incumbents’ moats before the capability is fully proven. The honest read: the tool is a preview. The fear was about trajectory, and trajectories reprice faster than products mature.
Bottom Line: Claude Code Security launched as a research preview and was priced like a category event — both things are true at once.
The February selloff: 15 billion dollars in hours
The Claude Code Security case study, dated and verified: on February 20, 2026, the research-preview launch sent cybersecurity stocks down sharply within a single session — the market loss exceeded $15 billion across the sector that day. The mechanism the reporting sketched: investors sold the workflows the tool threatens — the continuous-monitoring contracts, the triage and remediation services, the per-seat security products — on the logic that an AI system performing detection AND remediation drafts compresses (or replaces) large parts of existing security workflows and could hit growth and profitability across the category.
Why the repricing was rational — even if premature: the security industry’s revenue model is hours-and-seats: humans and licenses watching systems continuously. A tool that does the first pass of every alert, drafts fixes for every finding, and works at the speed of the model directly attacks the cost structure, even in research preview. Markets price trajectories: the preview proved the direction, and $15 billion was the market’s estimate of the revenue at risk if the direction holds. The counter-argument — security demand grows with every new attack surface AI creates — is the industry’s rebuttal, and both claims coexist in the same cycle: AI-native security competes with AI-era threats for the same future budget.
WorldNgayon Analysis: the February 20 case is the cleanest public example of the pattern the crash series documents generally: a single dated event repricing an industry’s moats in hours (the burst-timeline discipline runs on exactly this class of dated trigger). For security vendors, the February tape was a strategic memo: differentiate on what AI drafts cannot own — accountability, incident response, governance, the trust layer. For buyers: the repricing was the market handing you a better-negotiated renewal.
Bottom Line: $15 billion was the price of the market admitting AI security was no longer theoretical.
AI scanning vs static analysis: what actually changed
Three changes, ranked by consequence: 1 — reasoning over pattern-matching: the scanner evaluates cross-file logic (does this auth bypass actually bypass?) rather than matching dangerous shapes — which attacks the false-positive problem that makes classic SAST noisy, and the false-negative problem where novel logic bugs slip past signatures. 2 — remediation drafted, not recommended: the output includes code — a fix a reviewer can accept, edit or reject — collapsing the find-to-fix distance that human security teams spend days on. 3 — explanation of intent: the finding explains what an attacker would do with the bug, in language a product engineer reads — which upgrades the security conversation from scanner IDs to risk language.
What did NOT change: the need for runtime security (scanners read code, not production behavior), the governance layer (compliance, policy, audit trails), the human accountability model (a merge is still a human decision), and the attack surface itself — which AI is ALSO expanding (agents that write code introduce whole new bug classes). The honest scoreboard: the scanning tier got dramatically better; the security profession got more important precisely because its tooling got more powerful.
| Dimension | Classic SAST | AI reasoning scan (Claude Code Security class) |
| Detection style | Signature/rule matches | Contextual reasoning over the codebase |
| Output | Flagged lines + IDs | Findings in risk language + drafted fixes |
| False positives | High (rules cannot see intent) | Lower, but not zero — review still required |
| Novel-logic bugs | Often missed | Within reach (the launch’s differentiator) |
| Accountability | Vendor + team process | Unchanged: the merge decision stays human |
Bottom Line: the scanner got smarter, the merge decision did not move — that boundary is the product design.
The practical workflow: AI drafts, humans merge
The workflow teams converged on (the AI-security review discipline): 1 — scan on every pull request: run the AI scanner as a pipeline step; every finding arrives attached to the change that created the risk. 2 — triage by the finding’s explanation: the reasoning-model finding carries an attacker story — triage on the story’s plausibility, not the severity number alone. 3 — review the drafted fix like a code review: the drafted fix may be elegant and wrong (business logic the model cannot see); the reviewer owns the merge, and the ownership is not ceremonial. 4 — verify the fix did not open a new door: the fix itself needs the same scan it remediated — an AI-proposed remediation fixing one path and opening another is the class of bug the review layer exists for (the AI-verification discipline applies verbatim: verify the model’s claims against the artifact). 5 — log the human decisions: every accepted, edited and rejected AI fix is training data for your OWN security baselines — the teams that log the review trail build the auditable security record enterprises now ask for.
The skill this creates: AI-security-review fluency — the security engineer who can read an AI finding’s reasoning, judge its drafted fix, and document the decision is the profile this market pays up for (the account-security pieces and the injection-defense guides sit adjacent).
Bottom Line: the workflow writes itself: scan everything, read the stories, own the merges, log the trail.
The limits: what the research preview misses
Four live limits, honestly: 1 — preview-stage maturity: the February launch was a limited research preview — not general availability; capabilities, pricing and access changed after the launch windows. 2 — the business-logic blind spot: reasoning over code still cannot see your BUSINESS (that a discount below 10% requires approval, that this endpoint is internal-only); business-logic misuse remains a domain the reviewer must carry. 3 — the AI-misses-it failure mode: passing an AI scan is not proof of safety — the absence of findings is the weakest signal in security; defense in depth (runtime protection, audits, pen-tests) stays. 4 — supply-chain and infra layers: code-level scanning does not cover the dependency inventory, the infrastructure config, or the operational secrets — the scanner’s lane is the codebase.
WorldNgayon Analysis: the limits section is where the February panic meets the engineering reality: markets priced the trajectory; operators must price the actual tool. The discipline that resolves the gap is the claims discipline — vendor claims verified on YOUR codebase, severity triaged on YOUR business logic, and the residual risk owned where it always lived: with the human who merges.
Bottom Line: a preview-priced product, a business-logic blind spot, and an ownership rule — know all three before the tool touches your pipeline.
What this means for work, money and the Philippines
For careers: the security profession’s response to February was hiring, not cutting — the teams that ran the new tools needed reviewers who could judge them: AI-security-review and agent-security-verification are the new entry doors into the sector (the AI-jobs analyses carry the wage logic). For security vendors: the February tape rewrote the pitch — the survivors sell what AI scanning cannot: incident response SLAs, governance, audit trails, accountability.
For Filipino developers and OFWs: the tool runs on the platforms you already work in (Claude Code, the editor agents): the review workflow is learnable tonight and documents itself into your portfolio — “I ran and reviewed AI security scans on production codebases” is the 2026 interview line. The Philippines’ IT-BPM security-services slice (continuous monitoring, SOC work) reads the selloff as its own strategic signal: the monitoring tier is where AI compresses first — the upskill move is toward verification, incident response and governance, the tiers where the human signature stays valuable. The structural jobs analyses carry the same conclusion from the employment data.
For investors: February taught the tape’s new grammar — single dated AI launches can reprice adjacent industries in hours. The watchlist discipline (the warning-numbers piece) applies: when a lab announces a capability that touches an industry’s revenue model, the repricing happens before the capability is mature.
Verdict: a force multiplier that repriced an industry
Claude Code Security, settled: a reasoning-based vulnerability scanner launched February 20, 2026 in research preview — reading codebases in context, drafting fixes, explaining risk — that wiped $15 billion from cybersecurity stocks in hours because it threatens the hours the security industry bills. The tool is a force multiplier with a human-owned merge gate; the limits (preview maturity, business-logic blindness, the AI-missed-it mode) are the engineering reality beneath the market fear. The February selloff was not the AI era’s excess — it was the tape repricing an industry’s moats on a trajectory it could finally see. Force multiplier, repriced industry — both are the same story priced from two sides.
Sources on the record: the WisdomTree selloff analysis · Anthropic newsroom.
Financial Disclaimer
This article is editorial analysis of publicly reported information, not investment or financial advice, and no outcome is promised. Statements are as reported by the named sources at the stated dates; verify before acting. Markets carry substantial risk.
- wisdomtree.com/us/insights/blog/disrupted-or-discounted-making-sense-… — the WisdomTree selloff analysis
- anthropic.com/news — Anthropic newsroom
External sources linked in this article, in order of first mention. Spotted an error or a broken link? Tell us.
Cite this pagePublished Nov 1, 2026
Agron, E. (2026, November 1). Claude Code Security: What Anthropic Launched and Why Security Stocks Fell. WorldNgayon. https://worldngayon.com/claude-code-security/
Agron, Edmon. “Claude Code Security: What Anthropic Launched and Why Security Stocks Fell.” WorldNgayon, 1 Nov. 2026, worldngayon.com/claude-code-security/.
Agron, Edmon. “Claude Code Security: What Anthropic Launched and Why Security Stocks Fell.” WorldNgayon, November 1, 2026. https://worldngayon.com/claude-code-security/.
Agron, E. (2026) ‘Claude Code Security: What Anthropic Launched and Why Security Stocks Fell’, WorldNgayon, 1 November. Available at: https://worldngayon.com/claude-code-security/.
E. Agron, “Claude Code Security: What Anthropic Launched and Why Security Stocks Fell,” WorldNgayon, Nov. 1, 2026. [Online]. Available: https://worldngayon.com/claude-code-security/
@online{agron2026claudecode,
  author       = {Agron, Edmon},
  title        = {{Claude Code Security: What Anthropic Launched and Why Security Stocks Fell}},
  year         = {2026},
  date         = {2026-11-01},
  organization = {WorldNgayon},
  url          = {https://worldngayon.com/claude-code-security/},
  urldate      = {}
}TY - ELEC AU - Agron, Edmon TI - Claude Code Security: What Anthropic Launched and Why Security Stocks Fell T2 - WorldNgayon PY - 2026 DA - 2026/11/01/ UR - https://worldngayon.com/claude-code-security/ Y2 - ER -
Cite the version you read; the page may be updated. Zotero and Mendeley can also import this page directly.