THE BOARD — Thursday, October 1, 2026 → Crypto Watch #007 (Special Ledger): The ₱6.60 GCash print has company tonight: a fresh BSP partial suspension of Coins.ph’s operator DCPay — and a global crypto crime dataset just crossed a line the Philippine e-wallet generation needs to read. This is the ledger that connects the two: what regulator containment, wallet-drainer economics, and the new crypto security baseline mean for a market where pesos, crypto, and remittances share one app screen.
Table of Contents
Key Takeaway
- 🏦 The containment is live: DCPay (Coins.ph’s EMI) is partially suspended — inbound InstaPay/PESONet blocked; outbound and QR Ph spending alive; crypto under Betur’s separate VASP license untouched by the order itself.
- 🔓 2026’s theft economics flipped: stealing keys now beats exploiting bugs — infrastructure/operational compromises are ~15% of incidents but ~76% of losses (TRM Labs H1 data).
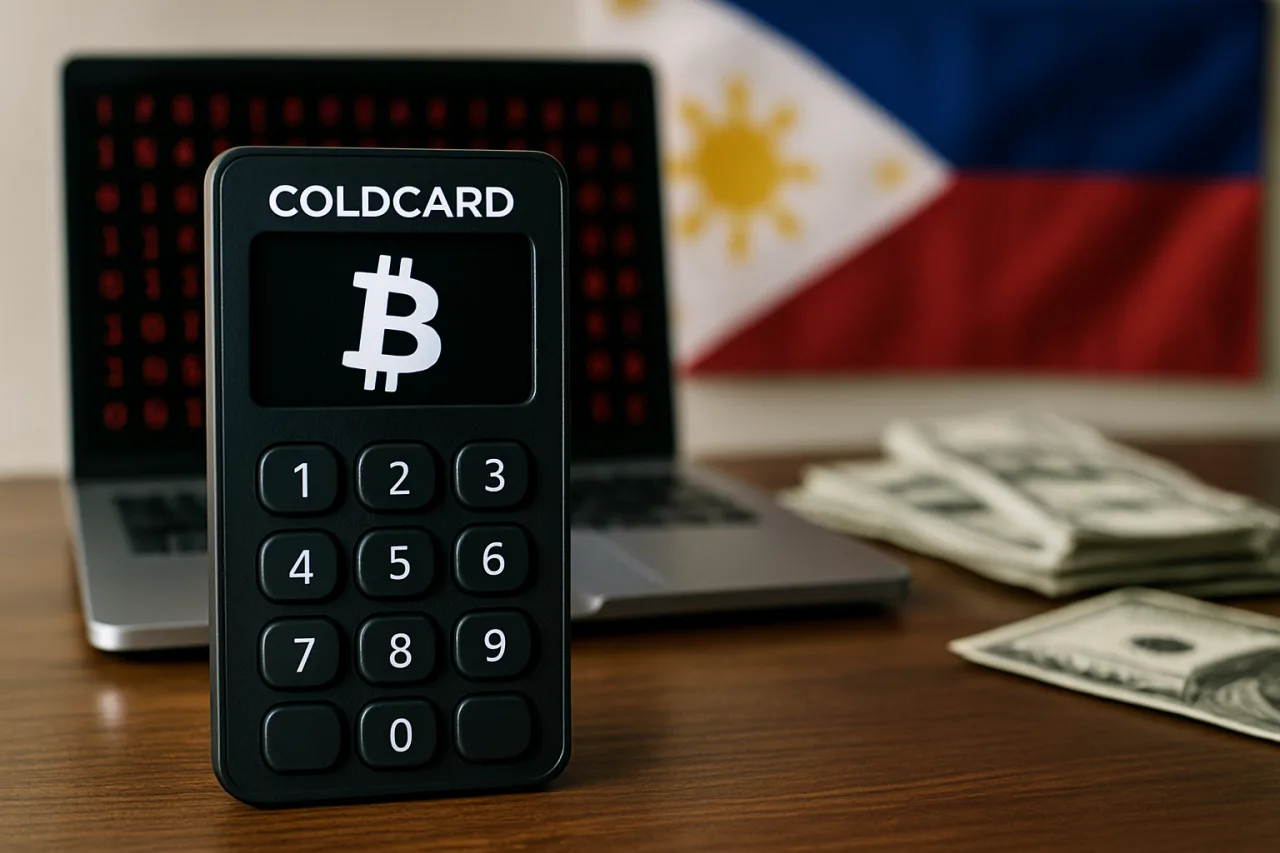
- 🧱 Hardware isn’t automatic armor: the Coldcard firmware flaw drained ~$116M (≈1,816 BTC) from devices sold years ago — entropy-era failures hit anyone who never rotated a seed.
- 🇵🇭 The OFW stack is the target surface: wallet + remittance app + IPO-week excitement = exactly the layered confusion drainers monetize. One screen, three risks.
- 🧭 The 6-lock routine below — from revoking permissions to the second-rail rule — is the minimum posture while the suspension window runs.
The DCPay Order, Read as a Crypto Security Event
The instrument chain is short: BSP Monetary Board Resolution No. 839 → PPMI Advisory No. 2026-0929-029 (September 29) → immediate implementation across InstaPay and PESONet. In practice — verified across BitPinas‘ advisory read and the Coins.ph status page — all inbound fiat rails to DCPay are frozen: cash-ins from BDO, BPI, UnionBank, GCash, and Maya reject at the rail. Outbound transfers remain authorized. QR Ph person-to-merchant spending continues. Crypto services under Betur Inc. keep operating — but the peso leg you’d use to fund a trade just lost its main bridge.
Why does a payments suspension belong in a crypto-security ledger? Because the failure mode it reveals is the one 2026’s theft data says matters most: operational chokepoints, not code bugs. DCPay wasn’t hacked. Nothing was “drained.” Yet millions of peso flows stopped moving the moment one regulator memo hit the clearinghouses — because an entire ecosystem of wallets, traders, and remittance users had concentrated its operational dependency on a handful of rails. Concentration is the vulnerability. The suspension simply demonstrated it without stealing a peso — the continuation of the enforcement arc this site mapped in the BSP-NTC crackdown guide.
The 2026 Theft Ledger: In Crypto Security, Keys Beat Bugs, Infrastructure Beats Everything
Two H1-2026 datasets (summarized in the 2026 exploit-statistics ledger) define the new baseline. TRM Labs recorded 207 incidents and $972M stolen in the first half — a record incident count, yet total losses below 2025’s pace, because the shape of theft changed: smart-contract exploits still lead raw incident counts (125 of 207), but infrastructure and operational compromise accounts for roughly 15% of incidents and 76% of the losses. CertiK’s parallel Hack3d report puts H1 2026 at $1.32B across 344 incidents — and its own analysts flag that removing one huge outlier still leaves losses higher than a year earlier. The direction is unambiguous: attackers stopped paying for code audits to be wrong and started paying for humans and infrastructure to be right.
Two case studies make the pattern concrete. In April, Drift Protocol lost ~$285M in twelve minutes — not through a contract bug but through a multi-jurisdiction social-engineering campaign in which attackers posed as a quant fund, met contributors in person, and even deposited real capital to build trust. Weeks later, Coldcard — literally the hardware-wallet category’s “paranoid” brand — gave up ~$116M (≈1,816 BTC from 5,200+ addresses) to a five-year-old firmware entropy flaw that had quietly reduced seed strength from 128 bits to as little as 40, per TRM Labs’ incident breakdown. Both attacks exploited the layers around the cryptography — the definition of the crypto security reset. That is the 2026 lesson in one line: your keys are only as secure as the operations and supply chain that produced and stored them.
For wallet-drainer economics specifically — the street-level crime most Filipino retail crypto users meet — the pattern is identical at smaller scale. Drainer kits like Inferno and Pink survive takedowns and resurface; the modern variants rarely need your seed phrase at all — the core fact of modern crypto security —, because they abuse token approvals (approve, setApprovalForAll, Permit/Permit2) — one careless signature and a wallet empties on schedule. Distribution rides fake airdrops, “support” DMs, and — new this year — AI-generated startup personas hosted on legitimate platforms (Notion docs, GitHub repos) that pass every surface-level credibility check.
Why the Philippines Is the Perfect Crypto Security Collision Zone Right Now
Stack the week’s facts and the risk geometry writes itself. The GCash IPO has created the year’s loudest fintech attention spike — millions of first-time investors, subscription budgets moving, price talk everywhere. In the same week, the BSP demonstrated it can freeze a major wallet’s inbound rails overnight (DCPay). Wallet-drainer kits are running their most productive stretch on record. And the country’s remittance-dependent households keep an average of multiple financial apps on one phone, with SMS, Messenger, and e-mail notifications layered on top. A crypto security analysis has one blunt read: the scammer’s perfect customer is not the naive; it’s the busy person with money in motion — and IPO week manufactures millions of them.
This is also where the two stories intersect operationally: a DCPay user whose cash-ins bounce today is exactly the person a “cash-in assistance” scammer wants — someone with real need, elevated emotion, and reduced official-channel patience. If any message, popup, or “agent” offers to reload your wallet for a fee during a regulator-ordered freeze, that’s not a workaround; it’s the drainer economy bidding for your business. The official lift arrives via new PPMI/BSP advisories — never via DM.
The 6-Lock Routine: Minimum Crypto Security While the Suspension Window Runs
- Lock 1 — Revoke your token approvals (10 minutes): use a revocation tool on your primary wallets every month, not just after a scare. Unclaimed standing permissions are the drainer economy’s inventory — the mechanics are exactly what this site dissected in the wallet-vulnerability teardown.
- Lock 2 — Retire any pre-2022 hardware seed you never rotated: the Coldcard case made “old firmware + old seed” a priced risk. If your device’s generation-era firmware ever shipped a weak-entropy release, migrate to a fresh seed on updated hardware before the next migration window closes.
- Lock 3 — Split custody by purpose, not by brand: long-term holds in hardware; trading float in a hot wallet; nothing personal in exchange accounts you wouldn’t mind frozen for review. The DCPay order showed why a single-rail balance is a single point of failure — even with no attacker involved.
- Lock 4 — Treat every signature as the transaction: read what you sign; Permit2 signatures can move tokens later without further prompts. If a site needs “unlimited” approval to “save gas,” it’s pricing your whole wallet for convenience.
- Lock 5 — Keep the second rail warm: whatever wallet/fintech apps your household uses, maintain a funded alternate path (bank + primary wallet + one backup EMI) so any freeze — regulator-ordered or platform-side — shifts payout in minutes, not days. This site’s digital-wallet licensing guide maps the licensed field, and today’s Coins.ph suspension playbook walks the operational choreography while the freeze runs.
- Lock 6 — Verify instruments before feelings: status page and official advisories first; social second; group chats last. The families that inverted that order this week were the ones a fake “lift order” popup could reach.
The North Korea Shadow, and Why Frequency Beats Size Now
One dataset note worth internalizing: TRM attributes roughly two-thirds of H1 2026’s stolen value (~$643M) to North Korea-linked operations, concentrated in two April attacks (Drift, Kelp DAO). Strip the state-actor outliers and per-incident losses look smaller — but frequency is higher, and the median victim is now a retail wallet, not an exchange. For a Philippine audience deciding where pesos, crypto, and remittances live, that inversion matters: the “it only happens to big exchanges” era is over; the 2026 crypto security threat model is you, your phone, your approvals. Frequency-scale theft is exactly what the 6-Lock routine is built to defeat — because it defeats the conditions — standing approvals, single-rail dependence, seed hoarding, trust-by-urgency — where crypto security actually fails rather than any single attack.
The Bridge Economics: What 2026’s Crypto Security Data Buys a Filipino Wallet Owner
Zoom out and the week’s three crypto security datasets — TRM’s $972M, CertiK’s $1.32B, and the Coldcard’s $116M — buy one practical purchase decision and one crypto security habit. The crypto security purchase: if you hold meaningful long-term crypto, the marginal peso is better spent on operational security (a fresh-seed hardware device on current firmware, a revocation routine, a second custody location) than on another exchange feature. The habit: a monthly 20-minute “ops review” — revoke stale approvals, update firmware, verify your second rail still works, re-read the standing instruments (status pages, official advisories) that your money depends on. None of it is glamorous; all of it attacks the 76%-of-losses category of crypto security instead of the 15%.
And a closing orientation for the fintech moment the Philippines is living through: the same week that showed a regulator can freeze the largest crypto-wallet’s inbound rails also showed global institutions re-committing billions to the country’s fintech future at ₱6.60 per share. Both facts describe the same maturing market — bigger stakes, sharper tools, less tolerance for operational naivety, on both the institutional and the household side of the screen. The generation that grew up “one app for everything” is being handed the 2026 version of the deal: more power, more reach, and a mandatory security layer that used to be optional. The six locks above are that layer, in the order that pays first.
One honesty note closes the ledger: crypto security is not a product you finish buying; it is a schedule you keep. The routines that matter — revocation, firmware checks, rail checks, signature reading — decay the way fitness decays: not all at once, but every week you skip them. The families that treat the ₱6.60 week and the DCPay freeze as their trigger date for the six locks turn a stressful news cycle into a permanent upgrade; the ones that treat it as content to scroll past will meet the next drainer kit on the same terms as this one. The instruments are public, the tools are free, and the time cost is one hour a month. In a market where a single regulator memo can freeze half of a wallet’s Monday — and a single signature can empty the other half — that hour is the highest-yielding investment in the entire stack.
Frequently Asked Questions
Is my cryptocurrency safe on Coins.ph during the BSP suspension?
Crypto custody and trading run under Betur Inc.’s separate VASP license, which is not the subject of the suspension order. What’s frozen is DCPay’s inbound fiat rails — so your holdings and trading functions stand, while your ability to cash in new pesos via InstaPay/PESONet is paused.
What’s the biggest crypto security risk for ordinary Filipino users in 2026?
Operational compromise — stolen keys, drainer-approved signatures, and social engineering — not smart-contract bugs. Infrastructure/operational failures were ~15% of H1 2026 incidents but ~76% of stolen value (TRM Labs).
Do hardware wallets protect against drainer scams?
Partially. They protect key custody, and blind-signing protections have improved — but approvals you sign remain valid, and the Coldcard case showed even hardware seeds can carry era-specific firmware risks. Rotate old seeds, read what you sign, revoke standing approvals.
Can someone drain my wallet with just my wallet address?
No. Address exposure allows tracking, not theft. Drainers need either your signature (approval phishing) or your key material (seed phrase/key theft) — which is why approval hygiene matters more than address privacy.
How do I recover from a wallet drainer?
Realistically: move surviving assets to a fresh wallet immediately (the approval may still stand on the old one), revoke permissions there, and report to platform security teams and PNP-ACE/PAOCC channels. “Recovery services” that DM you afterward are almost universally secondary scams.
Should I move my money out of Coins.ph because of the suspension?
If you want peso funds in a bank or primary wallet today, outbound transfers remain authorized — moving them is a normal operation, and reasonable while inbound rails are frozen. Decide on your own exposure and needs; just don’t act through anyone offering paid “cash-in assistance” during the freeze.
Financial Disclaimer
This article is for general information and security education only and does not constitute financial, legal, or investment advice. Regulatory actions and their practical effects can change without notice; verify current details through official BSP, PPMI, and platform channels before acting. The editor holds no position in any asset mentioned and is not affiliated with DCPay Philippines Inc. or Betur Inc.