Table of Contents
Key Takeaway
- 📊 The readiness gap: Only 16% of 670 in-scope business leaders surveyed say they are fully compliant, which means roughly 84% of the businesses in scope of NIS2 compliance are not finishers, not starters at the end, or still unsure what the law asks of them.
- ⚖️ Enforcement is live: Regulators in Germany, France, the Netherlands and Belgium are running audit programs and issuing formal orders, and on July 8, 2026 the European Commission referred four member states to the EU court for incomplete transposition.
- 🇧🇪 The template is set: Belgium requires third-party verified evidence and management sign-off; self-attestation is not accepted, and personal liability for management is built in.
- 💰 The blocker is budget, not understanding: yet 75% of surveyed firms see competitive advantage in compliance and 42% have been asked to prove it by a business partner.
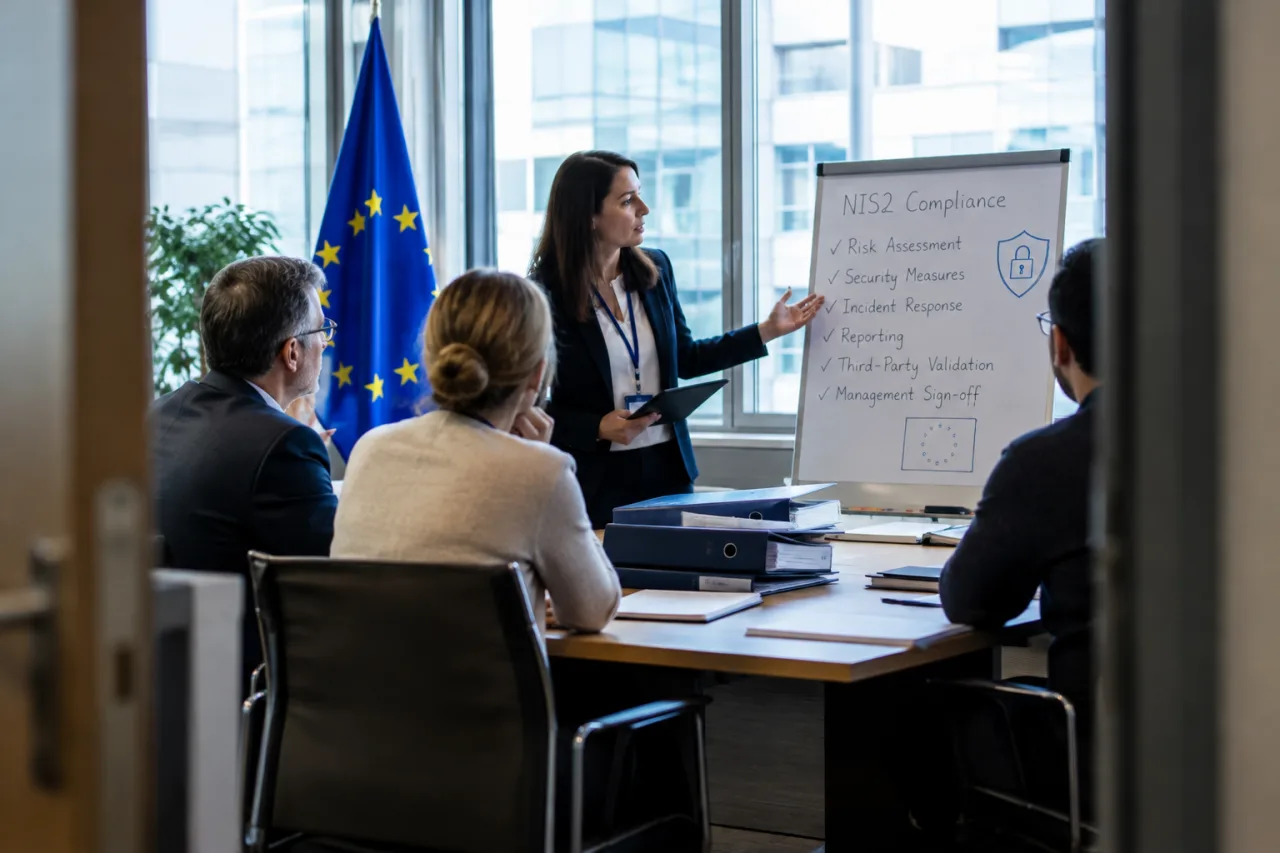
- 🧰 The fix list works in one afternoon: scope check, registration, an 18-point control map, evidence discipline and one reporting clock drilled into the team.
Only 16% of the 670 in-scope business leaders surveyed across nine European countries say they are fully compliant with the EU’s cybersecurity directive, and enforcement has switched on underneath that gap. Audits, formal supervisory orders and registration demands are moving through Germany, France, the Netherlands and Belgium, and on July 8, 2026 the European Commission referred Ireland, Spain, France and the Netherlands to the Court of Justice of the European Union for not finishing the job inside their own borders. If your company sits anywhere in the 18 regulated sectors, the afternoon spent on the fix list below is the cheapest NIS2 compliance you will ever buy.
NIS2 Compliance in 2026: What Enforcement Actually Looks Like
The story that circulated this summer, of headline fines landing everywhere, does not hold up. A review published in September 2026 checked the widely quoted figures in Belgium, Italy, Hungary and Lithuania against the regulators’ own publications and found no confirmed fine against a named company anywhere in the Union as of early September. What is confirmed matters more: supervisory orders number in the dozens across Germany and France, audit programs are active, and penalty schedules are published. The country pushing furthest is Belgium, where the Centre for Cybersecurity Belgium ran its first conformity cycle in April 2026: essential entities had to submit documentation verified by an accredited body or the authority itself, and self-declarations were rejected outright.
The second enforcement front in NIS2 compliance is the European Commission against its own member states. Transposition was due on October 17, 2024, and by April 2026 roughly 22 of 27 states had finished the job. In July 2026 the Commission escalated the laggards, referring Ireland, Spain, France and the Netherlands to the EU court. That matters to companies for a practical reason: in a country with incomplete transposition, the national rules you must follow are still stricter than you probably assume, because sector regulators are enforcing whatever their governments have already enacted.
Who Actually Has to Comply: Essential, Important and the 18 Sectors
The directive (EU) 2022/2555 splits organizations in scope into two tiers across 18 sectors. Essential entities carry the heavier obligations and supervision: electricity, transport, banking, financial market infrastructure, healthcare, drinking and waste water, digital infrastructure, managed technology services, public administration and space. Important entities cover the wide middle band: postal services, waste management, chemicals, food, manufacturing, digital providers and research organizations.
Size thresholds pull in far more companies than most owners expect: generally 50 or more employees, or more than 10 million euros in turnover, in a listed sector. The rule reaches subsidiaries and, critically, it reaches providers: a managed service provider counts by the nature of its business, not its headcount. A UK firm selling into EU clients can be pulled in by contract requirements even where local law has not caught up, which is exactly why surveyed leaders outside the Union track the same compliance wave.
Registration rules also differ by state, but the direction is uniform: authorities want to know who is in scope before an incident happens. Several governments opened national registries in 2025, and Belgium’s conformity cycle shows what comes after registration: evidence, not promises.
How Registration Works, and Where States Differ
Registration is the front door of NIS2 compliance, and it is where states diverge most. The directive obliges in-scope entities to register with the national authority, but each government set its own portal, deadlines and data requirements. What registration asks for is similar everywhere: legal identity, sector classification, contact points for incident communication, and sometimes an estimate of service scope. Several registries opened during 2025, and enforcement files since then show the pattern: firms that skipped registration receive the first orders.
The Belgian cycle is the reference case for what follows registration. Essential entities faced an April 18, 2026 deadline to produce conformity evidence verified by an accredited body or the authority itself, with management sign-off and personal liability attached. Self-declared spreadsheets were rejected by design. Treat that model as the direction of travel for the rest of the Union rather than local eccentricity.
The Obligations Behind the Orders: What the Directive Demands
Article 21 is the heart of NIS2 compliance, the section every auditor starts from. In plain terms, an in-scope company must maintain and periodically review a set of risk-management measures: a documented security policy with risk assessment, incident handling on defined procedures, business continuity with backup and disaster recovery, supply-chain security in the contracts with its own suppliers, secure acquisition and vulnerability handling, cryptographic and multi-factor controls where effective, and cybersecurity training for staff and management.
Article 23 sets the reporting clock that catches teams unprepared. A significant incident triggers an early warning within 24 hours, a formal incident notification within 72 hours, and a final report within one month. These clocks overlap with other regimes some firms already know, and the parallel is direct: what session hijacking means for a corporate cloud console is the same incident class these articles were written for.
Management liability is the third load-bearing wall. The directive makes senior managers accountable for approving the measures, overseeing implementation, and completing training. Belgium’s conformity documents carry management sign-off by design, and other states are following the same template. This is the provision that moves the topic from the IT budget into the boardroom.
The NIS2 Compliance Calendar That Already Ran
The deadlines most companies still assume are ahead of them are behind them. EU law set the transposition deadline for October 17, 2024, and the directive applied from the following day. In November 2024 the Commission sent formal notices to 23 member states over incomplete or delayed transposition. In May 2025 it escalated with reasoned opinions to 19 states. April 2026 brought Belgium’s first conformity-evidence deadline. July 8, 2026 brought the referrals of Ireland, Spain, France and the Netherlands to the EU court. The audit wave now running in Germany, France, the Netherlands and Belgium is the enforcement phase of a calendar that has been running for two years.
The Fix List: 9 Moves That Close the Gap
- Run the scope check in writing. Map your organization against the 18 sectors and the size thresholds, and record the decision. The scope memo answers the first question any auditor asks, and it settles the registration question.
- Register with your national authority if your state has opened the registry. Missing registration is the cheapest violation to commit and the easiest to prove.
- Map your controls against Article 21. Take the measure list, mark what exists as policy, what exists as practice, and what exists nowhere. That written gap map is the working document for everything else on this list.
- Buy third-party verification, not self-attestation. Belgium showed the template: accredited assessment and documented evidence. An annual audit that produces artifacts is what the conformity cycles accept.
- Assign ownership at board level. Management approval, oversight and training are statutory. Sixty percent of surveyed firms already put cybersecurity under the board; make yours formal with minutes, not informal with habit.
- Drill the reporting clock. Write the 24-hour, 72-hour and one-month deadlines into your incident plan with named owners. The teams that fail these clocks are the teams that improvise on the day.
- Put supply-chain security in the contracts. Article 21 reaches your suppliers. Update procurement language to require incident notification inside a defined window, which mirrors what the EU Cyber Resilience Act now demands from software vendors.
- Close the basics that audits weight heaviest: multi-factor authentication, tested backups, patch discipline and an inventory of the systems that matter. The small-business security checklist covers the same floor.
- Re-test every quarter. The measures must be reviewed periodically by law, and quarterly is the rhythm that keeps evidence current instead of manufactured before an audit.
Why Budget Is Not the Real Blocker
The same CyberSmart survey of 670 leaders, fielded in late 2025 and published in April 2026, offers a finding that changes the conversation: budget is the top reason firms cite for falling short, yet 75% see compliance as a competitive advantage and 42% have already been asked by a business partner to prove their posture. Eleven percent admitted they are not sure what the directive even is, which means the market’s problem is execution, not awareness.
Read those numbers against the cost of NIS2 compliance and the business case writes itself: the firms that finish early convert a legal burden into a sales qualifier, while the ones that delay keep paying for the same uncertainty in lost deals. The full survey is free to read and makes the partner-demand trend concrete.
What Happens If You Ignore It
NIS2 compliance failures carry penalty ceilings that national law implements: up to 10 million euros or 2% of global annual turnover for essential entities, and up to 7 million euros or 1.4% for important entities, whichever is higher. Supervisors also hold intermediate powers that bite sooner than fines: binding instructions, audit orders and, for persistent failures, suspension of certifications or of authorizations. None of this requires a breach to occur; the measures attach to the management systems themselves.
For the individual reader the practical exposure is narrower but real: personal liability for managers who fail to approve or oversee the measures. The safe reading of the 2026 enforcement posture is simple. The ceiling gets attention, but the floor is what companies actually trip on: registration, documentation and evidence discipline.
Frequently Asked Questions
Who must comply with NIS2?
Essential and important entities in 18 sectors, generally from 50 employees or 10 million euros in turnover upward, plus managed technology providers and digital suppliers. Subsidiaries and EU-selling foreign firms can be pulled in by national rules or contracts.
What are the NIS2 fines?
The ceilings are 10 million euros or 2% of global turnover for essential entities and 7 million euros or 1.4% for important entities, implemented by each state. Confirmed company-level fines remain rare in 2026; supervisory orders, audits and conformity requirements are the active instruments.
Is NIS2 enforcement actually happening?
Yes, in two forms: national regulators issuing registration demands, audit orders and formal supervisory measures, and the European Commission referring four member states to the EU court in July 2026 for incomplete transposition.
How much does NIS2 compliance cost?
No statutory fee schedule exists; the spend is in evidence, not tickets. Budgets go to a gap assessment, control remediation (multi-factor, backups, patching, logging), an accredited third-party assessment where the state requires one, and the periodic reviews the law mandates. Firms that map controls first commonly find the cheapest path is closing existing gaps rather than buying parallel tooling.
How long do I have to complete NIS2 compliance?
The NIS2 compliance deadline has passed; transposition was due October 17, 2024 and the directive applies since then. There is no grace period left, and the fix list above is the shortest route left. The question is not when compliance starts, but how fast the evidence can be produced.
What are the NIS2 incident reporting deadlines?
Early warning within 24 hours of awareness, full notification within 72 hours, and a final report within one month, per Article 23. The clock runs on the company’s own awareness, not the customer’s or the attacker’s.
What is the difference between NIS2 and GDPR?
The EU’s data-protection law governs personal data and privacy harm; NIS2 governs operational cybersecurity of critical services. One breach can trigger both: personal-data notification to a privacy authority, and incident notification to the cybersecurity authority, on different clocks.
If this intelligence helps you, you can add WorldNgayon as a preferred source on Google — free, one click, and it helps other Filipinos find the answers faster.
Financial Disclaimer
This article is published for general informational and educational purposes and does not constitute legal, financial, security-consulting or professional advice. Regulatory details current at publication may change; verify obligations against the directive text, your national transposition and your supervisory authority before acting. WorldNgayon and its author accept no liability for losses arising from the use or misuse of this information. Nothing here is affiliated or endorsed by any regulator, and no compensation was received for this article unless explicitly disclosed.
- passwork.pro/blog/nis2-latest-news-april-2026
- Official eur-lex.europa.eu/eli/dir/2022/2555/oj — The directive (EU) 2022/2555
- cybersmart.co.uk/nis2-research-2026 — full survey
- google.com/preferences/source?q=worldngayon.com — add WorldNgayon as a preferred source on Google
External sources linked in this article, in order of first mention. Spotted an error or a broken link? Tell us.
Cite this pagePublished Nov 11, 2026
Agron, E. (2026, November 11). 84% of EU Businesses Under NIS2 Enforcement Say They’re Not Ready — the Fix List. WorldNgayon. https://worldngayon.com/nis2-compliance-fix-list/
Agron, Edmon. “84% of EU Businesses Under NIS2 Enforcement Say They’re Not Ready — the Fix List.” WorldNgayon, 11 Nov. 2026, worldngayon.com/nis2-compliance-fix-list/.
Agron, Edmon. “84% of EU Businesses Under NIS2 Enforcement Say They’re Not Ready — the Fix List.” WorldNgayon, November 11, 2026. https://worldngayon.com/nis2-compliance-fix-list/.
Agron, E. (2026) ‘84% of EU Businesses Under NIS2 Enforcement Say They’re Not Ready — the Fix List’, WorldNgayon, 11 November. Available at: https://worldngayon.com/nis2-compliance-fix-list/.
E. Agron, “84% of EU Businesses Under NIS2 Enforcement Say They’re Not Ready — the Fix List,” WorldNgayon, Nov. 11, 2026. [Online]. Available: https://worldngayon.com/nis2-compliance-fix-list/
@online{agron2026nis2compliance,
  author       = {Agron, Edmon},
  title        = {{84\% of EU Businesses Under NIS2 Enforcement Say They’re Not Ready — the Fix List}},
  year         = {2026},
  date         = {2026-11-11},
  organization = {WorldNgayon},
  url          = {https://worldngayon.com/nis2-compliance-fix-list/},
  urldate      = {}
}TY - ELEC AU - Agron, Edmon TI - 84% of EU Businesses Under NIS2 Enforcement Say They’re Not Ready — the Fix List T2 - WorldNgayon PY - 2026 DA - 2026/11/11/ UR - https://worldngayon.com/nis2-compliance-fix-list/ Y2 - ER -
Cite the version you read; the page may be updated. Zotero and Mendeley can also import this page directly.