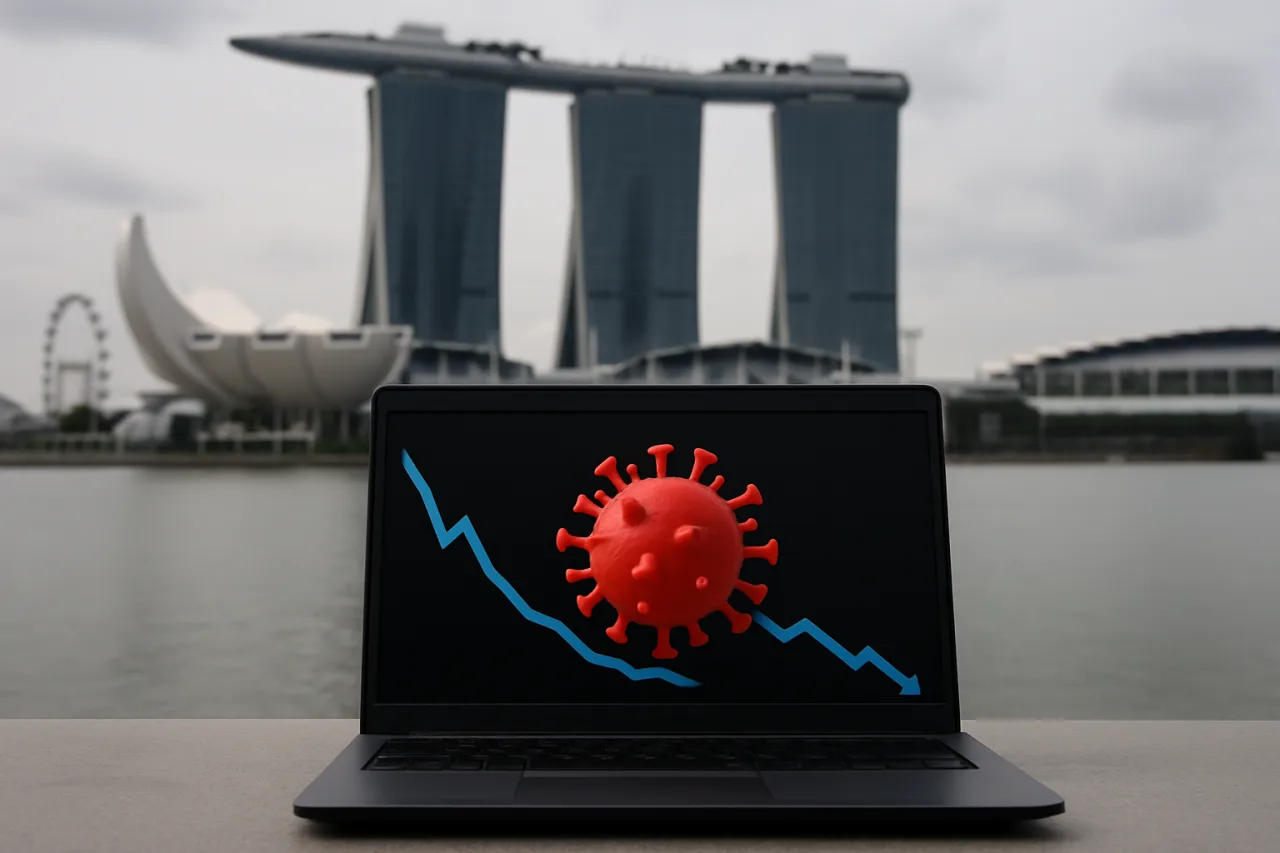
The 2025/2026 Singapore Cyber Landscape report, published June 30, marks the year Singapore’s infection curve inverted:
Table of Contents
systems infected by malware more than doubled over 2025, even as scam losses fell and advanced-persistent-threat groups traded disruption for stealth. Singapore Cyber Landscape 2025/2026 is the Cyber Security Agency’s own annual accounting — and read alongside the Singapore Cyber Landscape alert feed from this week (FortiMail’s 9.8 being exploited in the wild Monday, a local-vendor XSS Wednesday, Veeam’s 9.4 today), it draws the operating map of the city-state’s threat year: state espionage getting quieter, commodity malware getting louder, and the patch debt between the two growing in public. This analysis walks the report’s findings, connects them to this week’s CSA alerts, and prices what they mean for organizations and families in the corridor.
Key Takeaway
Treat the infection spike as the report’s central call to action: malware infections more than doubled while scams declined — enforcement bends the crimes it targets, patching debt grows where nobody is assigned to it. State espionage moved from disruption toward quiet credential accumulation; commodity malware industrialized; and the country’s countermeasures now form three coordinated layers (state, organizational, household) that a regional reader can copy at scale. This page is the corridor’s guide to the Singapore Cyber Landscape report — what changed, what did not, and what a Filipino family or business should actually do with the findings.
The infection spike: more than doubled, and why
The Singapore Cyber Landscape 2025/2026 report’s headline finding — locally infected systems more than doubled against the prior year — rests on two named drivers. Malware-as-a-Service turned the infection economy into a subscription business: credential-stealer kits and loader frameworks now rent by the week, which is why infection counts can double without any sophistication breakthrough, just cheaper distribution. The second driver is hardware Singaporeans own: consumer-grade IoT devices shipping with unpatched firmware or default passwords proliferated into homes faster than hygiene campaigns reached them. An infection curve that doubles while scam cases fall is not a contradiction; it measures two different crimes — one enforced down, one left to the patch cycle.
APT strategy: strategic optionality over disruption
The the Singapore Cyber Landscape report’s state-espionage finding is subtler than an attack count: APT groups have shifted toward accumulating credentials, preferring persistent network footholds over immediate disruption. The Singapore Cyber Landscape report projects 2026 state-sponsored activity will continue prioritizing access to critical information infrastructure for “strategic optionality” — the capability to act later, not the act today. The UNC3886 case made the pattern concrete:
publicly revealed in July 2025 after infiltrating Singapore’s critical infrastructure, the group’s attacks continued through this year, detected earlier each time as the defenders’ collaboration improved. CSIT’s chief confirmed this week that attacks persist but are “detected and dealt with more effectively than before,” with weak-signal sharing now formalized through the Digital Defence Hub — including the Google Cloud Security exchange agreement signed October 9.
This week’s alerts, read against the report
Three CSA alerts in four days (October 6-9) illustrate the report’s thesis live. Monday: FortiMail CVE-2026-104286 — CVSS 9.8, unauthenticated path traversal, actively exploited, with Fortinet’s advisory confirming in-wild exploitation; the four-month patch timeline echoes the Roundcube lag this site analyzed with the Simba breach.
Wednesday: SQLView KRIS CVE-2026-89191, a contained 6.8 stored-XSS fixed through CSA’s responsible-disclosure process — the same week a local vendor patched two months after disclosure, showing the coordination machine working. Today: Veeam Backup & Replication CVE-2025-64393 — CVSS 9.4, remote code execution via the Backup Viewer role, versions 12 through 12.3.2.4854 affected. Backup infrastructure is the crown-jewel target: whoever owns the backup console often owns the recovery option of the entire company. Three alerts, three lesson types: patch velocity, disclosure hygiene, and backup privilege discipline.
The ransomware line: still climbing
Alongside the infection spike, the Singapore Cyber Landscape analysis reports ransomware attacks increased in line with global trends — no local exception to the region’s pressure. The correlation the report quietly establishes: the same MaaS distribution that doubled infections feeds ransomware crews’ initial access, and the same unpatched IoT estate gives them footholds. For Singapore organizations the report’s message lands differently than for consumers: the scam decline the police brief celebrates offers no comfort to an IT team, because the two threat pools do not share victims. A company that spent 2026 fighting fraud found itself ahead on the scam curve and exposed on the malware curve — the report exists to end that complacency.
What CSA built in 2025 — the counter-measures map
The Singapore Cyber Landscape’s second half catalogs the year’s institutional build-out: initiatives to strengthen cyber defenses of critical information infrastructure and organizations, and awareness programs for individuals, from the cybersecurity-matters toolkit for households to the sector-specific hardening of CII operators. The architecture is layered deliberately: state coordination (CSIT’s Digital Defence Hub, sensors inside CII networks), organizational pressure (incident-reporting harmonization now expanding through the Digital Infrastructure Bill passed October 7), and individual hygiene (the household-level campaigns). Readers who want the full picture can walk the agency’s own publications shelf; the corridor analysis below translates the report’s architecture into Filipino-relevant terms.
The corridor translation: what the report moves for Filipinos
Three transfers land. First, the infection doubling is a household warning with a corridor twist: OFW families run the highest IoT density of any demographic in their income class — the routers, CCTV cameras and smart devices connecting three homes across two countries — and the same default-password problem the report names multiplies across every device installed remotely by a relative in Manila for a family in Singapore.
Second, the credential-accumulation APT strategy touches OFW records directly: identity rows (the NRIC-class data exposed in the Simba breach) are exactly the persistent-foothold currency state groups collect — and the same rows fuel the bank-impersonation scams hitting Filipino households. Third, the patch-discipline lesson transfers whole: Singapore’s doubling infections are the result of unpatched convenience, the same debt the Philippines’ agencies keep warning about — the corridor’s homes share the firmware, so they share the fix schedule.
The alert feed as a dataset: what a year of CSA notices teaches
The report is annual; the alert feed is weekly — and the two read together best. CSA’s alert format (product, CVE, CVSS exploitation status, version ranges, one-line action) has become the corridor’s fastest vulnerability signal, and its cadence itself is information: email-infrastructure flaws (Roundcube, FortiMail), backup-platform flaws (Veeam this week), and locally adopted products (SQLView KRIS) show where the city-state’s real attack surface concentrates. An administrator who reads only vendor bulletins sees products; the CSA feed prices the same flaws with local exploitation context. For Filipino IT teams running Singapore-facing services, monitoring the CSA feed alongside the local CERT advisories costs nothing and closes the visibility gap this report documents growing.
The Digital Infrastructure Bill: the report’s legislative sequel
Days before this analysis, Parliament passed the Digital Infrastructure Bill (October 7) — the report’s threats written into statute. Data centres above 10 megawatts of critical IT load and cloud providers earning at least S$100 million annually from Singapore users will need foundational-digital-infrastructure licences covering physical security, continuity and cyber-incident reporting to IMDA and CSA, with penalties up to S$1 million or 10% of Singapore turnover.
About two-thirds of the country’s 70 data centres fall inside the regime. The bill operationalizes the report’s “systemic infrastructure” concept: platforms whose failure now equals national disruption get statutory floors. The regional signal is bigger than the rules — Singapore is codifying cloud-and-datacentre resilience as core-of-government territory, and ASEAN regulators (including the Philippines’ own DICT infrastructure reviews) will read the bill as a template.
The household layer: what the toolkit actually asks
The report’s individual-facing recommendations resolve to a short, verifiable list: default passwords changed within first setup (the IoT estate’s highest-value fix), firmware updates on a schedule rather than on failure, separate credentials for high-stakes accounts, and the ScamShield suite for the fraud half of the threat map. None of it requires paid tooling — and that is the report’s most underrated finding: the doubling infection curve grew on free fixes left uninstalled. A household that executes only the default-password sweep removes the majority of the attack surface the report documents growing; the corridor’s remittance-guarding families should treat that one action as the year’s highest-return security task.
Two household truths in the Singapore Cyber Landscape deserve the corridor’s specific translation because they cost nothing and repeat everywhere. The first: the strongest infection driver in the report is distribution cost, not exploit novelty — Malware-as-a-Service exists because infection pays by the mailbox, and every unprotected mailbox funds the next kit.
A family that removes one default password starves that model more than any awareness poster ever will; the Singapore Cyber Landscape economics turn hygiene into sabotage of the criminal supply chain. The second: the report’s own architecture — state, organization, household — assigns each layer a job rather than blame; the corridor version assigns the OFW worker the household layer, the BPO/finance employer the organizational layer, and reads the state layer as the coordination to demand from agencies. None of the three layers can carry the other two; the Singapore Cyber Landscape map’s genius is refusing to let any actor consider the problem handled.
Scoreboard: what improved and what worsened
The report’s ledger splits cleanly. Improved: scam-case and loss numbers (the police brief’s domain), weak-signal sharing between stakeholders, CII sensor coverage, disclosure coordination with vendors. Worsened: infections (doubled), ransomware (climbing with global trend), the credential footprint of the average household (more devices, more accounts, more firmware debt). Flat: state-espionage pressure (continuous, quieter). That ledger is the honest output of a mature cyber state — Singapore does not claim the tide turned; it claims enforcement works where aimed, and the report prices the rest in public. Corridor readers comparing national positions should note the method: name the worsening as precisely as the improving. Regional neighbors’ scorecards that report only wins read as marketing, not measurement.
The report’s readers most often miss one methodological note, and it matters for every cross-country comparison this corridor makes: the Singapore Cyber Landscape measures what Singapore’s own instrumentation sees — signals from CII sensors, incident reports, and coordination partners — so its infection figures measure reported instrumented observations, not a census of every compromised device.
A doubling on that baseline is still a doubling in real signal; but the number’s meaning (‘what our monitoring caught’) differs from what a lay reader assumes (‘how many computers were infected’). Every statistic this site republishes from the report carries that qualifier, and readers benchmarking Singapore against the Philippines’ DICT disclosures — or any ASEAN neighbor’s figures — should compare methods before magnitude. A mature document invites exactly this scrutiny; the Singapore Cyber Landscape publishes its collection basis in the same pages that publish its findings.
One forecast closes the analysis with the report’s own posture. The threats that doubled — commodity infection, ransomware pressure — respond to boring maintenance; the threats that quieted — state disruption — respond to coordination. Singapore’s 2025/2026 year proves both levers work because both were pulled simultaneously. The corridor’s test is whether the same two levers can be pulled in systems with thinner resources; the replicable part is not the budget, it is the assignment of responsibility — every device owned by someone, every flaw fed to a disclosure channel, every scorecard publishing its worsened column. The Singapore Cyber Landscape report will re-run annually; the corridor’s scorecards should, too.
How to read this analysis
WorldNgayon maintains this as a dated companion to the report cycle: updated when CSA publishes the next Singapore Cyber Landscape edition or when the alert feed signals a trend shift; verification date below; slugs frozen. Companion pieces on the same shelf: the FortiMail zero-day coverage, the Simba breach analysis with the Roundcube wave, and the Philippines breach statistics hub — the corridor’s two national pictures, infection economics and disclosure economics, cross-referenced.
Primary sources: the Singapore Cyber Landscape 2025/2026 (CSA, June 30, 2026); this week’s alerts AL-2026-133, AL-2026-138; the Digital Infrastructure Bill explainer (MDDI); and CSIT’s weak-signals briefing (Straits Times, October 9, 2026). Last verified: October 9, 2026.
How to cite this page
Cite as: Worldngayon, “Singapore Cyber Landscape 2025/2026: The Infection Spike Behind the Scam Decline,” 2026. Analysis verified against CSA’s published report and alert feed; all external claims traced to agency documents or named briefings.