Table of Contents
Key Takeaway
- 📈 Ransomware across Asia-Pacific jumped 26.7% in a single month: Group-IB logged 190 attacks in August 2026 inside a 695-threat month, and Southeast Asia’s public and industrial sectors are carrying a visible share of the load.
- 🇲🇾 Malaysia recorded more than 30 confirmed ransomware incidents in the first half of 2026, one of the region’s highest counts, and the pattern is operational disruption rather than dramatic disclosure.
- 🏭 The regional profile matters: SEA’s $800-billion-plus digital economy grew faster than its security base, so attackers monetize downtime at factories, ports, utilities, and government counters instead of chasing headlines.
- 🛡️ The survival core is boring and proven: 3-2-1 backups with one immutable or offline copy, tested at least quarterly, layered with MFA everywhere, prompt edge-device patching, and a rehearsed response plan.
- ✅ Tonight-action: check today (not next week) whether your backups ever failed restore, whether MFA covers remote access, and whether the newest internet-facing devices received their patches.
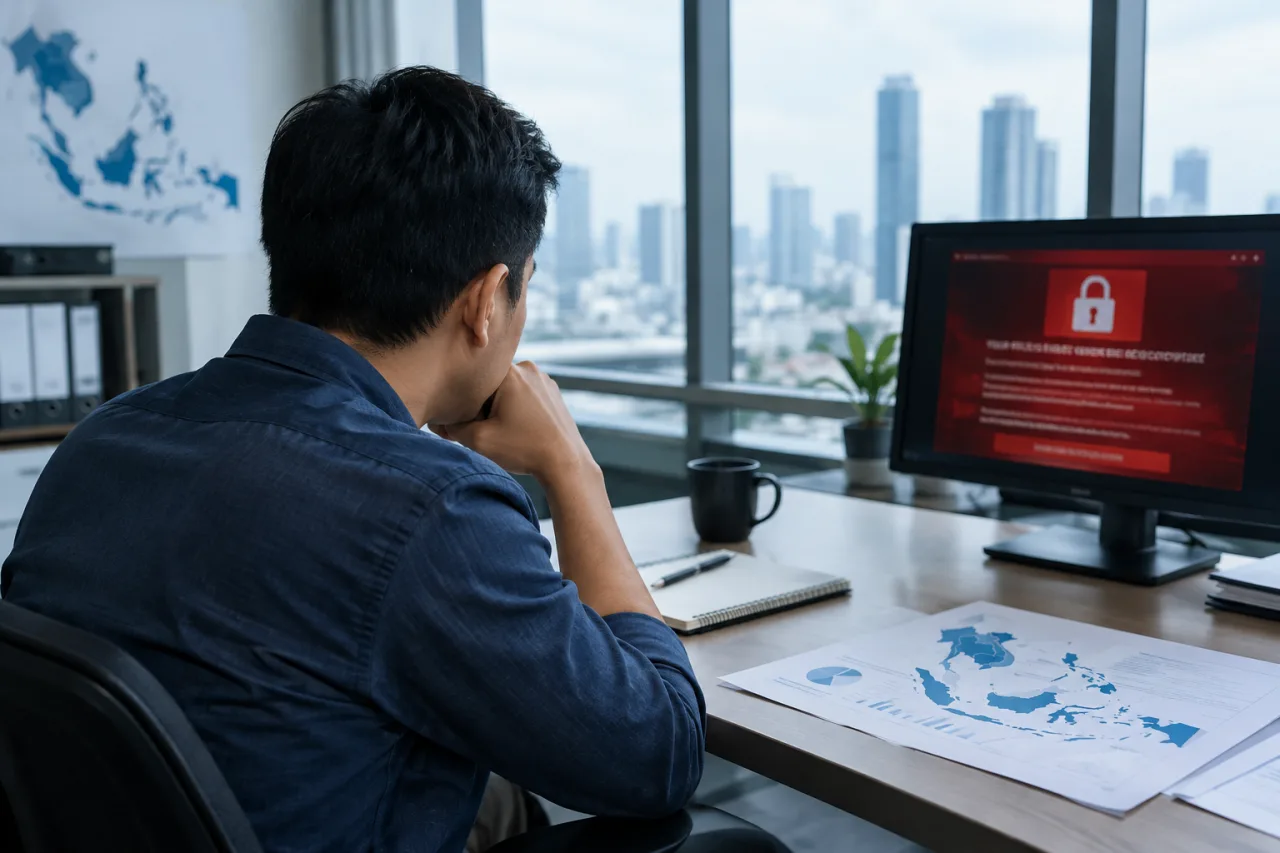
Ransomware in Southeast Asia no longer looks like the loud, leak-heavy campaigns that dominate Western headlines. The regional record shows a quieter but heavier pattern: fewer announcements, more shutdowns. Group-IB’s August 2026 census logged 190 ransomware attacks across Asia-Pacific in one month, a 26.7% rise on July, inside a 695-threat month overall, and the incident notes skew toward manufacturing, government, energy, and transport. Malaysia’s first-half count exceeds thirty confirmed incidents. The economics are simple: a region running an $800-billion digital economy on growing but thinner defenses offers attackers maximum downtime value per intrusion. This guide lays out where the hits land, why the regional pattern differs, and the survival checklist that cuts the damage, written for business owners and IT teams deciding where their next hour of mitigation budget goes.
Ransomware in Southeast Asia: the Numbers Behind the Pattern
The monthly telemetry shows direction, not just volume. Group-IB recorded 190 ransomware attacks across APAC in August 2026, up 26.7% from July, with the total threat count reaching 695 incidents in 31 days, per the Group-IB APAC Threat Landscape Report. The report names freshly emerged groups operating in the region and notes that ransomware grew while other categories stayed flat, meaning the increase reflects operator focus, not background noise.
Country tracking firms the picture further. Malaysia logged more than thirty confirmed incidents in the first half of 2026, placing it among the region’s most targeted markets, per the Malaysia H1 2026 ransomware report, and the sector spread concentrates on manufacturing and services firms that keep operations running on older Windows estates and flat networks. Across the wider region, government entities in Indonesia, Singapore, Malaysia, the Philippines, Vietnam, and Thailand report sustained escalation in attacks on public systems, a pattern the regional press has tied to digital-service growth without a matching security-hiring curve.
Our regional coverage already tracks the wider industrial base feeding this: the infrastructure boom documented in our Southeast Asia AI infrastructure analysis multiplies the number of high-value targets, and the scam-industry economics in the AI scam compounds guide explain where operational skills come from.
Why the Regional Ransomware Pattern Differs from the West
Three structural differences shape what SEA victims experience:
- Operational disruption over disclosure. Western incidents surface through SEC filings and leak-site posts. SEA ransomware concentrates on stopping work: production lines, cargo handling, ticketing, and land-registry counters. Fewer public announcements does not mean fewer incidents; it means the damage shows up in output, not in data-leak tallies.
- The edge-device front door. VPN concentrators, NAS boxes, camera systems, and routers shipped with unpatched firmware provide quiet entry points. The global October record documented in our ransomware record analysis already tied record victim counts to edge-device exploitation, and SEA’s large installed base of older edge hardware makes the same door the regional default.
- Payment complexity. Regional insurers are thinner, cyber policies rarer, and recovery teams farther between. That pushes victims toward fast payments on favorable terms for attackers, and it makes the prevention checklist on this page worth more here than a negotiation strategy.
None of this means the region is doomed. It means the order of operations differs: detection and containment investments outrank negotiation budgets, and the checks below are ordered accordingly.
The Before-State: the Six Checks That Decide the Outcome
Survival is decided before the intrusion starts. Six checks, in the order most teams skip them:
- Immutable backups, proven by restore. The 3-2-1 rule (three copies, two media, one offline or immutable) only counts if a quarterly restore actually worked. An untested backup is a hope, not a control.
- MFA on every external door. Remote desktop, VPN, admin panels, cloud consoles. One credential-pair without MFA is the single most common intrusion route named in post-incident reports.
- Edge-device patching within days, not quarters. VPN concentrators and NAS firmware get exploited within days of disclosure. Assign devices owners and patch dates, and keep an inventory.
- Least privilege, no shared admin. Domain-wide admin accounts turned the average intrusion into a full-network encryption event. Segmented admin rights cap the spread at the first compromised host.
- Email filtering plus the human drill. Most intrusions begin with one convincing document. Our infostealer check guide shows the five-minute audit that catches the credential theft feeding these campaigns.
- A written, rehearsed response plan. The five-step plan documented in our incident-response guide turns panic into sequence: isolate, preserve, notify stakeholders, restore from clean images, review entry point. Teams that rehearse lose days, not months.
Inside the Regional Attack Machine: Who Runs These Campaigns
The crews behind the regional numbers resemble franchises more than hacker collectives. Access brokers sell entry into one company to encryptors who never met the original intruder; negotiators with call-center training run the payment conversations; leak-site editors publish proof folders when talks stall. The regional twist is the reuse of scam-industry talent: the same compound economies documented in our fraud-industry coverage supply the human operators, and turnover is measured in weeks. That labor model explains two patterns in the data. First, attack quality tracks operator experience: campaigns repeat the same exploitation of unpatched VPN gateways and NAS panels because new hires re-run the last campaign script, which means yesterday’s advisory remains next week’s intrusion. Second, ransom demands in the region often scale by visible revenue signals rather than database size, since the business model is downtime, not data. Understanding the machine’s shape keeps defenses pointed at the right seams: the entry device, the admin path, and the backup’s network reach.
The counterweight is equally organizational. Regional CERTs now publish advisories weekly, insurers in Singapore and Malaysia price the controls instead of the industry, and the gap between attacked and defended firms is closing fastest where an owner, not a committee, signs the patch schedule. The machine bets on drift; the checklist wins by refusing to drift.
The During-State: the First 24 Hours If Encryption Hits
If ransomware activates, the sequence matters more than the software:
- Isolate the affected segment now. Pull network cables, disable Wi-Fi and VPN profiles, and quarantine shared drives. Speed here decides whether the damage stays at one department or reaches the domain.
- Preserve evidence before any wipe. One disk image of a compromised host supports insurer claims, law-enforcement reports, and later forensic review. Wiping everything first destroys the record of how entry happened.
- Contact the national CERT or cybercrime line. Regional agencies (CyberSecurity Malaysia, Indonesia’s BSSN, the Philippines’ CICC, Singapore’s SingCERT) issue containment guidance and track sector campaigns; reports also feed the regional data that shapes the next round of advisories.
- Restore from the verified clean copy, not the newest one. Backups that were mapped or encrypted alongside the network restore the attacker’s persistence. The restore point predating the intrusion, virus-scanned and volume-shadow-clean, is the safe path back.
- Do not negotiate on the attacker’s schedule. If a payment decision ever lands, it happens after containment, with counsel and insurer input, never under the double-deadline threat in the ransom note.
After the Incident: the 30-Day Rebuild List
Recovered systems fail again unless the entry point closes. The 30-day list: reset every credential exposed by the compromise; patch or replace the exploited device; close the flat-network segments the encryption traversed; convert one backup tier to immutable storage; schedule the first quarterly restore test; and document the full timeline for the insurer, the regulator where breach-notification duties apply, and the next rehearsal. Businesses that complete this list convert the incident into their strongest year of security investment; teams that skip it reappear in someone’s next statistics report.
The Government Layer Beneath the Businesses
Regional institutions shape what businesses face. The public-sector escalation documented across the six major economies lands on services citizens touch daily, from permit counters to hospital systems, and pushes national budgets toward SOC capacity and sector CERTs. NIST’s ransomware outcomes framework, updated as IR 8374r1 in June 2026, gives regional IT teams a vendor-neutral checklist that reads cleanly against the controls above, from governing and identifying through recovering. The practical takeaway for an SEA business: when your national agency issues an advisory on a named exploit, treat it as an incident-prevention memo with a deadline, because the regional attack statistics show the campaigns arrive within weeks.
What the Numbers Miss: the Undercount and Why Reporting Changes It
Every statistic on this page deserves one caveat: the true regional count is higher than any published number. Disruption-only attacks that end in a quiet restore never touch a leak site, insurers settle under confidentiality clauses, and smaller firms report nothing at all, so the visible figures understate both volume and sector spread. The reporting gap cuts both ways: victims underreport because disclosure feels expensive, and the underreporting starves the national agencies that defend the next victims of pattern data.
The fix is procedural, not heroic. Reporting a ransomware attempt through the national cybercrime line takes minutes, keeps the firm anonymous in aggregate statistics, and feeds sector advisories that protect suppliers and customers inside the same supply chain. The firms that report fastest are also the ones whose insurers pay fastest, because the paper trail exists. Over time, the region’s counter-ransomware capability is built by exactly this loop: incidents reported, patterns named, advisories issued, edge devices patched before the next wave. A business that joins that loop this year is safer than its identical neighbor that decided it had nothing worth reporting.
A line for the owners deciding tonight: ransomware readiness is mostly an inventory problem. You cannot protect a device you never listed, back up a database someone forgot, or patch firmware whose vendor page nobody checks. The six-check list is short because it is really one longer question asked six ways: do we know, precisely, what we run and who can reach it? Teams that can answer in a page usually survive the month the statistics describe; teams that need a week to compile the list have already found their first gap, and that discovery, made today, is the cheapest security purchase they will ever make. Start the page tonight with the machines everyone forgets: the printer with a web console, the CCTV recorder reachable from the office network, the laptop that only appears at month-end. Write each one down, check its patch date, and hand the list to a named person with a named date. That single page, reviewed quarterly, is the difference between a business that reads regional threat reports as headlines and one that reads them as maintenance schedules.
FAQ
How bad is ransomware in Southeast Asia right now?
The verified telemetry shows sustained growth: 190 APAC ransomware attacks in August 2026 alone, a 26.7% month-over-month rise inside a 695-threat month, per Group-IB, with Malaysia logging more than 30 confirmed incidents in the first half of 2026. The regional toll likely exceeds public leak-site counts because disruption-only attacks often go unreported.
Which sectors get hit hardest in the region?
Manufacturing, government, energy, transport, and services dominate the incident notes, because their downtime converts directly into losses and they often run older operational networks. Public-sector attacks cluster around digital services whose outages cancel citizen transactions rather than leak dramatic data.
What is the single highest-value ransomware control?
Immutable, tested backups. Everything else reduces the odds; backups decide whether an incident is measured in hours or months. The tested part matters as much as the immutable part, since unmaintained backup paths get mapped and encrypted by the same hands that encrypted production.
Should a Southeast Asian business pay the ransom?
The plain answer is: payment funds the next campaign and the reliability of any decryption tool remains the attacker’s choice. Containment, national-reporting channels, and verified clean restores have carried more organizations back than payments have, and the decision, if one ever comes, belongs with counsel and insurers, after containment, never on the ransom note’s deadline.
How do attackers get in if the staff never clicks anything?
Through the machines no one considers staff devices: unpatched VPN concentrators, exposed NAS panels, forgotten cameras, and edge routers. The 2026 pattern shows more intrusions starting at the network edge than at the inbox, which is why patch discipline on internet-facing equipment outranks another phishing slideshow.
What should I do this week, concretely?
Run the six-check before-state list in order, starting with a restore test on one backup set and an MFA audit on remote-access doors. Where a check fails, fix that item first; the order above reflects how post-incident reports rank what actually decided the outcome.
- group-ib.com/resources/research-hub/apac-threat-landscape-report-augu… — Group-IB APAC Threat Landscape Report
- simplydata.com.my/malaysia-ransomware-report-h1-2026 — Malaysia H1 2026 ransomware report
- Official csrc.nist.gov/pubs/ir/8374/r1/final — updated as IR 8374r1 in June 2026
External sources linked in this article, in order of first mention. Spotted an error or a broken link? Tell us.
Cite this pagePublished Nov 12, 2026
Agron, E. (2026, November 12). Ransomware in Southeast Asia: the 2026 Landscape and the Survival Checklist. WorldNgayon. https://worldngayon.com/ransomware-southeast-asia/
Agron, Edmon. “Ransomware in Southeast Asia: the 2026 Landscape and the Survival Checklist.” WorldNgayon, 12 Nov. 2026, worldngayon.com/ransomware-southeast-asia/.
Agron, Edmon. “Ransomware in Southeast Asia: the 2026 Landscape and the Survival Checklist.” WorldNgayon, November 12, 2026. https://worldngayon.com/ransomware-southeast-asia/.
Agron, E. (2026) ‘Ransomware in Southeast Asia: the 2026 Landscape and the Survival Checklist’, WorldNgayon, 12 November. Available at: https://worldngayon.com/ransomware-southeast-asia/.
E. Agron, “Ransomware in Southeast Asia: the 2026 Landscape and the Survival Checklist,” WorldNgayon, Nov. 12, 2026. [Online]. Available: https://worldngayon.com/ransomware-southeast-asia/
@online{agron2026ransomwaresoutheast,
  author       = {Agron, Edmon},
  title        = {{Ransomware in Southeast Asia: the 2026 Landscape and the Survival Checklist}},
  year         = {2026},
  date         = {2026-11-12},
  organization = {WorldNgayon},
  url          = {https://worldngayon.com/ransomware-southeast-asia/},
  urldate      = {}
}TY - ELEC AU - Agron, Edmon TI - Ransomware in Southeast Asia: the 2026 Landscape and the Survival Checklist T2 - WorldNgayon PY - 2026 DA - 2026/11/12/ UR - https://worldngayon.com/ransomware-southeast-asia/ Y2 - ER -
Cite the version you read; the page may be updated. Zotero and Mendeley can also import this page directly.