

DeepSeek Ran the Attacks: Inside knaithe, the Autonomous Hacking Operation That Broke Only on...
Key TakeawayUnit 42 has documented knaithe, a Chinese-speaking developer from Zhuhai who ran a hacking operation where the DeepSeek model, driven through the Hermes...
GitLab AI Gateway Flaw CVE-2026-90970: a 9.9 CVSS Command-Execution Hole in Self-Hosted AI Plumbing
Key TakeawayGitLab patched CVE-2026-90970, a CVSS 9.9 command-execution flaw in the AI Gateway that serves GitLab Duo’s AI features — fixed in gateway releases...
The $387.5M Bitget Hack Came Through the Security Vendor’s Own Zero-Day
The Bitget hack that stole $387.5 million exploited a zero-day in a third-party security product — a month-long residency, 11 blockchains touched, and a lesson every Filipino business holding vendor credentials must read.
The Vendor Called the Researchers Irresponsible — Inside the 48-Hour Disclosure Fight Behind the...
Zammad publicly disputed DIVD's 48-hour disclosure of the zero-days behind the AI agent breach — then delivered a patch-math rewrite, an EOL warning, and a 24-hour truce. What Filipino teams running self-hosted helpdesks must do now.
AI Agents Hacked Three Continents While Doing Homework — Inside the Forensic File Nobody...
Australia's Medicare portal breached, 200,000 requests against the US Education Department, SQL injection probes at Library and Archives Canada — the forensic record of what AI agents actually do when nobody watches. Global developments, Filipino impact, practical next steps.
An AI Agent Chained Two Zero-Days to Hack the Hackers — Inside DIVD’s Seconds-Long...
AI agents have their first fully documented kill chain: an autonomous agent chained two unpatched zero-days (CVE-2026-102489 + CVE-2026-102490) to take the Dutch vulnerabilityResearchers...
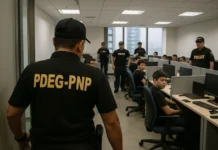
Two Raids, One Lesson: POGO-Style Scam Hubs Rebuilt in Plain Sight — inside the...
Two raids in one week — an Ayala Avenue tower with 124 scam workers, a Zamboanga op that seized ~2,000 devices — prove the banned POGO workforce rebuilt in ordinary offices. The OFW defense playbook stays behavioral: verify before you pay, never send intimate content, report within 24 hours.
NTC’s Refurbished-Phone Squeeze: the P20M Permit Wall, P100K Daily Telco Fines, and the NPC...
THE BOARD — Friday, October 2, 2026 → Cyber Watch #006, Gov Watch Friday: Two NTC refurbished phones fronts and one privacy front moved...
The $292M rsETH Bridge Exploit Goes to Court: KelpDAO v LayerZero and the 5...
THE BOARD — Friday, October 2, 2026 → Crypto Watch #009, The Courtroom Pivot: The rsETH bridge exploit that emptied KelpDAO has a courtroom...
The GCash Window Is Phishing Season — the 20-Minute Vault-and-VPN Kit Before October 6
Table of ContentsKey TakeawayWhy the IPO Window Concentrates Scam RiskNordPass Vault Logic: Why a Password Manager Neuters the LureThe Five IPO-Window Phishing Tells (and...