Table of Contents
Key Takeaway
- 📉 Cyber insurance is getting cheaper and broader in Southeast Asia’s most mature market: the Straits Times reported on September 13, 2026 that coverage in Singapore is widening while premiums fall, as eight insurers compete for a growing SME base.
- 🧾 The qualifier list is short and knowable: insurers now expect proof of multifactor authentication on admin, email, and remote access, tested backups, endpoint detection, patching discipline, and staff training, before they quote, per the 2026 industry requirement trackers.
- 💰 Mid-market coverage remains rare: only around 10 percent of SMEs globally carry cyber insurance, and the share is thinner in parts of Southeast Asia, which is exactly why fresh quotes are landing better for firms that qualify.
- 🦁 The policy is a checklist product: the exclusions that bite are known categories (phishing transfers, unpatched systems, undeclared breaches), so a business that fixes the qualifier list first often buys twice the cover for the same premium.
- ✅ Tonight-action: run the five-control audit before you ask for the quote, document it, and read the social-engineering clause twice, because that is where SME policies win or lose claims.
Cyber insurance crossed from a niche for multinationals into a usable SME product in Southeast Asia this year, and the move happened quietly in the quote sheets before it showed up in the press. The Straits Times’ September 13, 2026 report put numbers on the shift in Singapore: coverage widening, premiums falling, brokers seeing renewed appetite, and the competition among insurers now working in the customer’s favor, per the Straits Times report. This guide explains what cyber insurance actually contains, what insurers demand before they will quote an SME, where the exclusions hide, and how a small business in the region goes from uninsured to insurable in one working quarter, with the financial-advice caveat up front: this is market orientation, not a quote, and your broker prices your real risk.
The context matters for the timing. The region recorded sustained ransomware pressure through 2026, the threat landscape our Southeast Asia ransomware guide tracks month by month, and cyber insurance underwriters price the controls that stop those intrusions far more generously than they price promises. A business that arrives at a broker with the controls documented buys cheaper; a business that asks first and fixes later pays the panic premium.
What Cyber Insurance Actually Pays For
A typical SME cyber insurance policy bundles several pays that a general liability product does not touch:
- Incident response: forensic investigators, a legal team, and notification support from the insurer’s panel, activated within hours of the call.
- Business-interruption loss: income lost while systems sit down, the line that matters most in a region where disruption-heavy attacks are the dominant pattern.
- Restoration: the cost of rebuilding systems and data from clean copies after an encryption event.
- Liability: third-party claims and regulator-facing costs when customer data leaks, the area where data-protection statutes across the region raise the stakes.
- Extortion response: negotiation and, where lawful and approved, extortion-payment cover, always the smallest line and the most caveated.
The differences between cyber insurance policies usually live in the sublimits: how much of the limit is reserved for each line, what the waiting period is before business-interruption pays, and whether the response panel is the insurer’s choice or yours. Reading those numbers matters more than reading the headline limit.
The Five Controls Insurers Demand Before Quoting
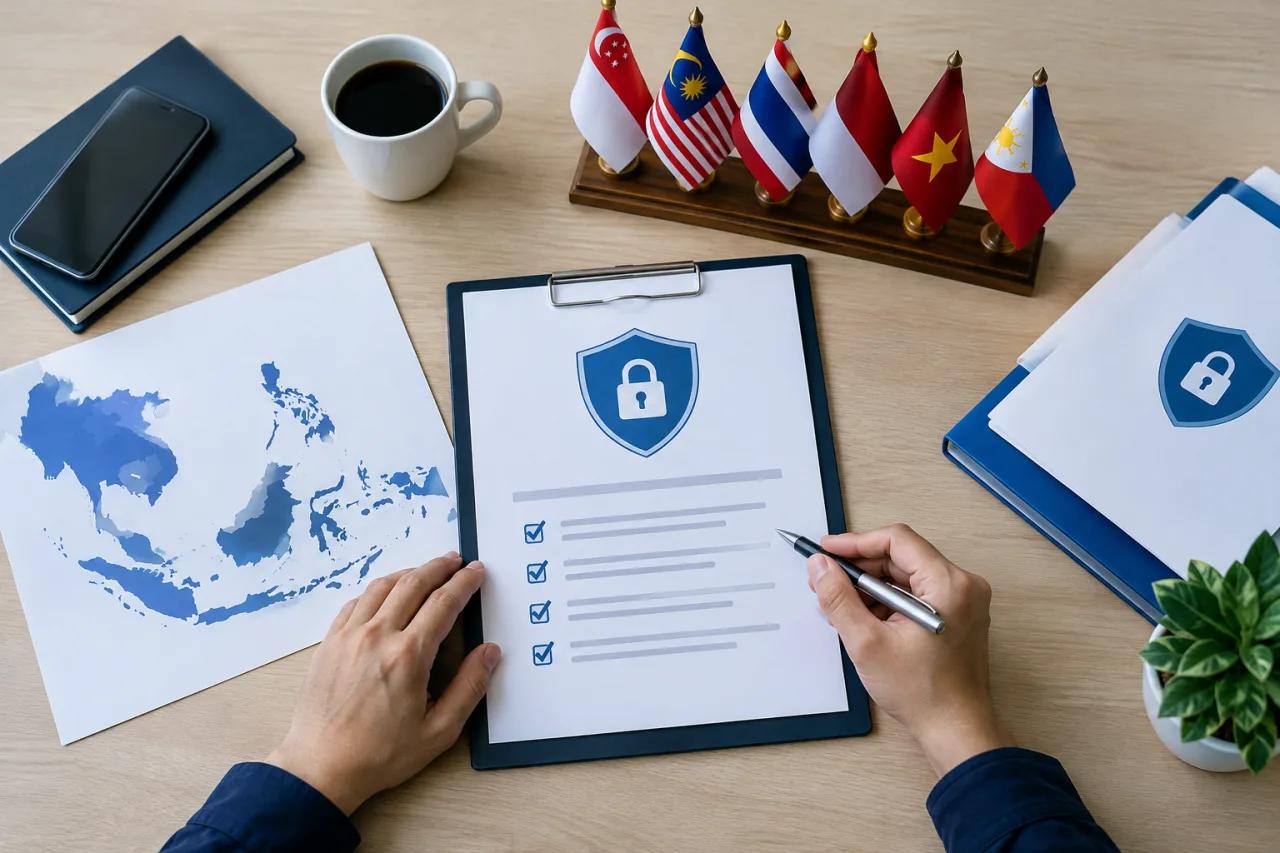
The 2026 requirement lists across brokers converge on five controls, and they double as the region’s best-practice baseline:
- Multifactor authentication on admin accounts, email, and remote access, with no standing exceptions. The single most-asked question in the quote form, because credential theft drives the claims file.
- Tested, offline or immutable backups. Insurers increasingly ask for evidence the restore was actually run, not just configured, which mirrors the survival checklist in our ransomware guide.
- Endpoint detection and response on the machines that matter, replacing legacy antivirus-only answers.
- Patching discipline on the internet-facing estate, with the edge devices (VPN, NAS, cameras) named in an inventory.
- Staff training and an incident plan. The human layer, evidenced by dated training records and a rehearsed response document, which is the same plan our incident-response guide walks through in five steps.
The small-business baseline for each item already exists in our small-business security checklist, which means the qualifier list and good hygiene are the same list. That is the quiet design of the insurance market: it pays you, in premium, to fix what you should have fixed anyway.
What It Costs, in Current Numbers
Premiums moved down in Singapore’s most competitive segment this year, per the Straits Times reporting, while coverage widened, and the forces behind that movement matter for readers outside Singapore too: more insurers entered the SME pool, loss ratios improved as baseline controls spread, and product standardization made quotes comparable. Mid-market and SME coverage across the wider region still runs thin, at around 10 percent of SMEs insured globally by some industry estimates and thinner in parts of the region, per the KnowBe4 mid-market analysis. Thin markets price conservatively until controls data arrives, which is why the Singapore pattern (more controls, more quotes, falling premiums) is the template the region’s insurers copy.
For planning purposes: SME policies are annual products whose premiums scale with revenue, industry, data volume, and the control posture documented at application, and quotes vary widely on the same revenue, which is exactly why the documented-controls approach moves the number. Get two or three broker quotes with the audit attached; the spread between them is the negotiation.
Where the Exclusions Hide
Four clauses decide most SME claims, and each is preventable:
- The social-engineering clause. Transfers made by an employee fooled into paying a fraudulent invoice sit in a sub-limit line, sometimes excluded, sometimes requiring the “verified by call-back” control to be evidenced. This is the most-read clause after an invoice scam.
- The unpatched-systems clause. Claims arising from a vuln patched months before the incident can draw reduction. The patch inventory doubles as the claim’s defense, and the device-label shopping guide covers why the installed base matters.
- The war and state-actor carve-outs. Attribution fights live here; read the definition of “war” in your policy, because it is broader than the dictionary’s.
- The prior-breach clause. Undeclared incidents before the policy start void lines of cover. Declare history plainly with your broker; it is cheaper than the dispute.
The practical rule for an SME owner: have the broker walk your actual scenario, the fake-invoice transfer, the encrypted file server, the leaked customer database, against the draft policy line by line before signature. Ten minutes of scenario reading beats a year of assumptions.
The Regulatory Layer the Policy Sits On
Regional regulation is tilting toward documented cyber hygiene, which makes the insurable base easier to prove. Singapore’s Cybersecurity Agency concluded the public consultation on its cybersecurity service-provider licensing updates, with implementation scheduled progressively from January 2026, per the REACH consultation record, and the updated Cybersecurity Code of Practice for critical information infrastructure landed on July 29, 2026, per the Stephenson Harwood analysis. The pattern for insurers: regulated hygiene turns application questionnaires from honor statements into checkable facts, and that is what makes premiums fall in a market. Businesses in the region can read the Singapore trajectory as the road ahead for their own markets’ brokers.
Cyber Insurance Exclusions: Reading the Contract Like an Owner
The exclusions page is where cyber insurance either becomes your recovery partner or a receipt for money spent. Read it against four realistic evenings, not against the definitions of art. Evening one: the fake-invoice transfer, and ask the broker which clause answers a social-engineering payment. Evening two: the encrypted file server, and ask which line pays the rebuild when the entry point was an unpatched edge device. Evening three: the leaked customer database, and ask how the regulator-facing costs flow and whether notification letters count toward the limit. Evening four: the business-interruption week, and ask the exact waiting period with its clock in hours. A broker who walks these four with you is a broker worth keeping, and a policy that answers them clearly is one worth its premium, because exclusions are not traps: they are the priced boundary of what the controls your application promised can prevent. The pattern to hold: the qualifier list protects you twice, once as security and once as the boundary the exclusions respect.
The claims process itself rewards preparation. Policies typically obligate the insured to notify promptly, to cooperate with the insurer’s response panel, and to preserve evidence; the paperwork runs smoother when the incident-response plan already names who calls whom in the first hour. Businesses that keep a printed contact card (broker hotline, panel contacts, national CERT) recover on other people’s playbooks, which is the point of the premium.
The Four-Week Path From Uninsured to Insurable
One working month, sequenced:
- Week 1: run the five-control audit and document each with a screenshot or policy export; name the gaps plainly.
- Week 2: close the cheap gaps (MFA everywhere, backup immutability, patch inventory), fix nothing exotic yet.
- Week 3: assemble the pack for a broker: revenue, industry, data types, the control evidence, and the two incident scenarios you want the policy priced against.
- Week 4: take two to three quotes, read the four exclusions in each, scenario-test the draft with the broker, and bind the policy that answers your real risks, not the one with the biggest headline number.
Businesses that follow this sequence usually discover the same thing the market data shows: the controls were mostly affordable, the cover was mostly available, and the gap between them was a quarter of focused work.
Financial Disclaimer: This article is general market information about a business insurance category and is not financial or insurance advice, and not an endorsement of any insurer or product. Coverage, premiums, and eligibility vary by insurer, jurisdiction, and your circumstances. Read the actual policy wording and consult a licensed insurance broker or adviser before purchasing.
Two planning notes close this guide. First, the market moves with the regional ransomware numbers: every quarter of elevated attacks reprices the SME pool, so a quote taken this quarter is a better price than the same quote taken after a bad quarter, and the documented-controls pack you assembled holds its value across renewals. Second, the renewal is where the relationship pays: insurers reward demonstrated year-over-year control maturity with better terms, which converts the security program from a cost center into a negotiating asset. Write the control report once a year, walk it through the renewal, and the premium conversation changes tone at the table.
One caution for the comparison shopper: the same control evidence can price differently across insurers because each weights its recent claims differently, so the cheapest quote is not automatically the value quote. The value read sits in the sublimits, the waiting periods, and the list of what the response panel will actually do in the first 24 hours. Price the promise, not just the premium.
FAQ
Is cyber insurance worth it for a small business in Southeast Asia?
For businesses holding customer data or running revenue-critical systems, the coverage economics changed in 2026: premiums fell in the region’s most competitive market while the control requirements overlap almost entirely with the security baseline a good operator should run anyway. Get a documented-controls quote from two brokers and the numbers usually make the case themselves.
What does a cyber insurance policy pay for?
The core lines are incident-response costs, business-interruption income loss, system restoration, third-party liability including regulator-facing costs, and a tightly caveated extortion-response line. The real differences between policies sit in sublimits per line, the waiting period before interruption cover pays, and who controls the response panel.
What do insurers require before quoting an SME?
The 2026 requirement lists converge on: multifactor authentication on admin, email, and remote access; tested backups with an offline or immutable copy; endpoint detection on key machines; documented patching on internet-facing systems; and evidence of staff training plus a written incident plan.
Why did premiums fall in Singapore?
The Straits Times reported on September 13, 2026 that coverage widened and premiums fell as eight insurers competed in the segment. The mechanics: more underwriters with better regional claims data, standardized SME products, and a customer base whose baseline controls improved, which lowered loss ratios and made quotes comparable.
Does insurance pay out on invoice scams and social engineering?
Sometimes, and the clause decides it. Social-engineering losses typically carry their own sublimit, may require evidence of verification controls such as call-backs, and in some products remain excluded. Read that clause against your realistic scenario before binding, and install the call-back habit either way, since it prevents the loss that the clause was written about.
How do I start if my business has no cyber controls documented?
Start with the four-week path: audit the five controls, close the cheap gaps in week two, assemble the qualification pack in week three, and take competing quotes in week four. The controls double as your insurance qualification file and your defense against the regional ransomware pattern, so nothing in the month is wasted work.
- straitstimes.com/tech/cyber-insurance-gains-ground-in-singapore-as-co… — Straits Times report
- blog.knowbe4.com/cyber-insurance-for-mid-market-organizations-in-sout… — KnowBe4 mid-market analysis
- Official reach.gov.sg/latest-happenings/public-consultations/2025/consultation… — REACH consultation record
- stephensonharwood.com/insights/singapores-csa-issues-updated-cybersec… — Stephenson Harwood analysis
External sources linked in this article, in order of first mention. Spotted an error or a broken link? Tell us.
Cite this pagePublished Nov 12, 2026
Agron, E. (2026, November 12). Cyber Insurance for SMEs in Southeast Asia: What It Now Costs and What It Covers. WorldNgayon. https://worldngayon.com/cyber-insurance-southeast-asia/
Agron, Edmon. “Cyber Insurance for SMEs in Southeast Asia: What It Now Costs and What It Covers.” WorldNgayon, 12 Nov. 2026, worldngayon.com/cyber-insurance-southeast-asia/.
Agron, Edmon. “Cyber Insurance for SMEs in Southeast Asia: What It Now Costs and What It Covers.” WorldNgayon, November 12, 2026. https://worldngayon.com/cyber-insurance-southeast-asia/.
Agron, E. (2026) ‘Cyber Insurance for SMEs in Southeast Asia: What It Now Costs and What It Covers’, WorldNgayon, 12 November. Available at: https://worldngayon.com/cyber-insurance-southeast-asia/.
E. Agron, “Cyber Insurance for SMEs in Southeast Asia: What It Now Costs and What It Covers,” WorldNgayon, Nov. 12, 2026. [Online]. Available: https://worldngayon.com/cyber-insurance-southeast-asia/
@online{agron2026cyberinsurance,
  author       = {Agron, Edmon},
  title        = {{Cyber Insurance for SMEs in Southeast Asia: What It Now Costs and What It Covers}},
  year         = {2026},
  date         = {2026-11-12},
  organization = {WorldNgayon},
  url          = {https://worldngayon.com/cyber-insurance-southeast-asia/},
  urldate      = {}
}TY - ELEC AU - Agron, Edmon TI - Cyber Insurance for SMEs in Southeast Asia: What It Now Costs and What It Covers T2 - WorldNgayon PY - 2026 DA - 2026/11/12/ UR - https://worldngayon.com/cyber-insurance-southeast-asia/ Y2 - ER -
Cite the version you read; the page may be updated. Zotero and Mendeley can also import this page directly.