Table of Contents
Key Takeaways
- On October 12, 2026, the data-theft extortion group n0n posted 38 maritime and logistics organizations on its leak site in a single batch — and ZPMC, the world’s largest port machinery maker, is on that list.
- Nothing is confirmed. None of the 38 named organizations had publicly confirmed a breach as of the October 13–14 reporting, and every “stolen data” description is the attacker’s own claim.
- SOCRadar, the cybersecurity firm tracking the group, reviewed demands between USD 2.4 million and USD 14 million, all pointed at one publish deadline: October 19, 2026, 13:27 UTC.
- The ZPMC entry claims operational EDI archives and cargo loading records — electronic cargo paperwork, claimed by the attacker, verified by no one.
- If your business exchanges electronic cargo data with any named company, this week is for mapping your shared systems and rotating integration credentials — the full checklist is below.
ZPMC — the Chinese company that builds a large share of the world’s container cranes — is named on a ransom leak site, and the countdown on its entry runs out on October 19. A data-theft extortion group calling itself n0n says it holds operational records from ZPMC and 37 other maritime organizations, and it set a single publication deadline for the whole batch: October 19, 2026, at 13:27 UTC. If your cargo, your employer or your client book touches a terminal that uses ZPMC cranes and systems, this is your story to read with care.
The honest headline is the uncomfortable one: nothing here is confirmed. What exists is a leak-site post, a deadline engineered to create fear, and a cybersecurity firm’s analysis of the group behind it. This article separates the claim from the confirmation, then gives port-side and logistics businesses the checklist worth running before the deadline passes.
The October 12 Signal: 38 Companies, One Countdown
Per SOCRadar’s maritime analysis, n0n added 38 organizations to its leak site in one batch on October 12, 2026: container terminals, shipping lines, port IT providers, and logistics businesses across 18 countries. ZPMC (China) appears in the list’s adjacent-industry row, beside companies from Singapore and South Korea. The Loadstar and PortNews carried the same batch with the same framing, and The Loadstar summarized the shared detail: none of the listed organizations had confirmed anything at the time of writing.
The deadline is the loudest number. Every maritime entry is set to publish on October 19, 2026, at 13:27 UTC — a uniform seven-day window. SOCRadar reads that uniformity as unusual, because the group’s earlier releases rolled out in a staggered rhythm; a single synchronized date is consistent with the batch being processed at once, which keeps open the possibility of a shared data source behind the 38 claims. SOCRadar says the reviewed ransom demands run from USD 2.4 million to USD 14 million across the batch.
The listed data descriptions are specific in the way extortion listings usually are. Per The Loadstar’s review of the leak-site samples, entries claim electronic data interchange (EDI) messages, container manifests, vessel schedules, gate movements, and terminal system configuration records, with claimed volumes from 60 megabytes to 2.4 gigabytes. South Korea accounts for 12 of the 38 entries, including Busan terminal operators BNCT and Pusan Newport Company.
Who Is n0n? Seven Weeks Old, Mostly Claims So Far
n0n surfaced in September 2026 as a financially motivated data-theft extortion group, likely based in Russia, according to SOCRadar’s tracker profile. Its model departs from the classic ransomware playbook: the group generally avoids deploying encryption malware and instead threatens to publish stolen data unless paid. SOCRadar notes the profile still carries techniques associated with encryption and recovery interference, so defenders should not rule out disruptive action — but the group’s weapon so far has been the leak threat itself.
Its track record is the reason for calm arithmetic. Before the maritime wave, n0n listed 21 victims as of October 8, 2026. Nineteen of those stayed at the claimed stage, one was marked negotiating, and only one — the IT services firm Chibitek — actually experienced a published data leak. In other words: so far, n0n’s claims have largely stayed claims, which is exactly the lens to bring to the ZPMC entry.
One more detail matters for the whole cluster. SOCRadar’s hedged line is that initial access was likely an exposed shared application or vulnerability rather than 38 separate network intrusions — small, application-scoped data sets and incomplete infostealer coverage across victims point that way. The Loadstar notes the pattern resembles the MOVEit 2023 and Cleo 2024 file-transfer campaigns, while reporting that SOCRadar found no evidence n0n ran a mass-exploitation method here. Treat the shared-system theory as a possibility under study, not a finding.
Why ZPMC Matters in This List
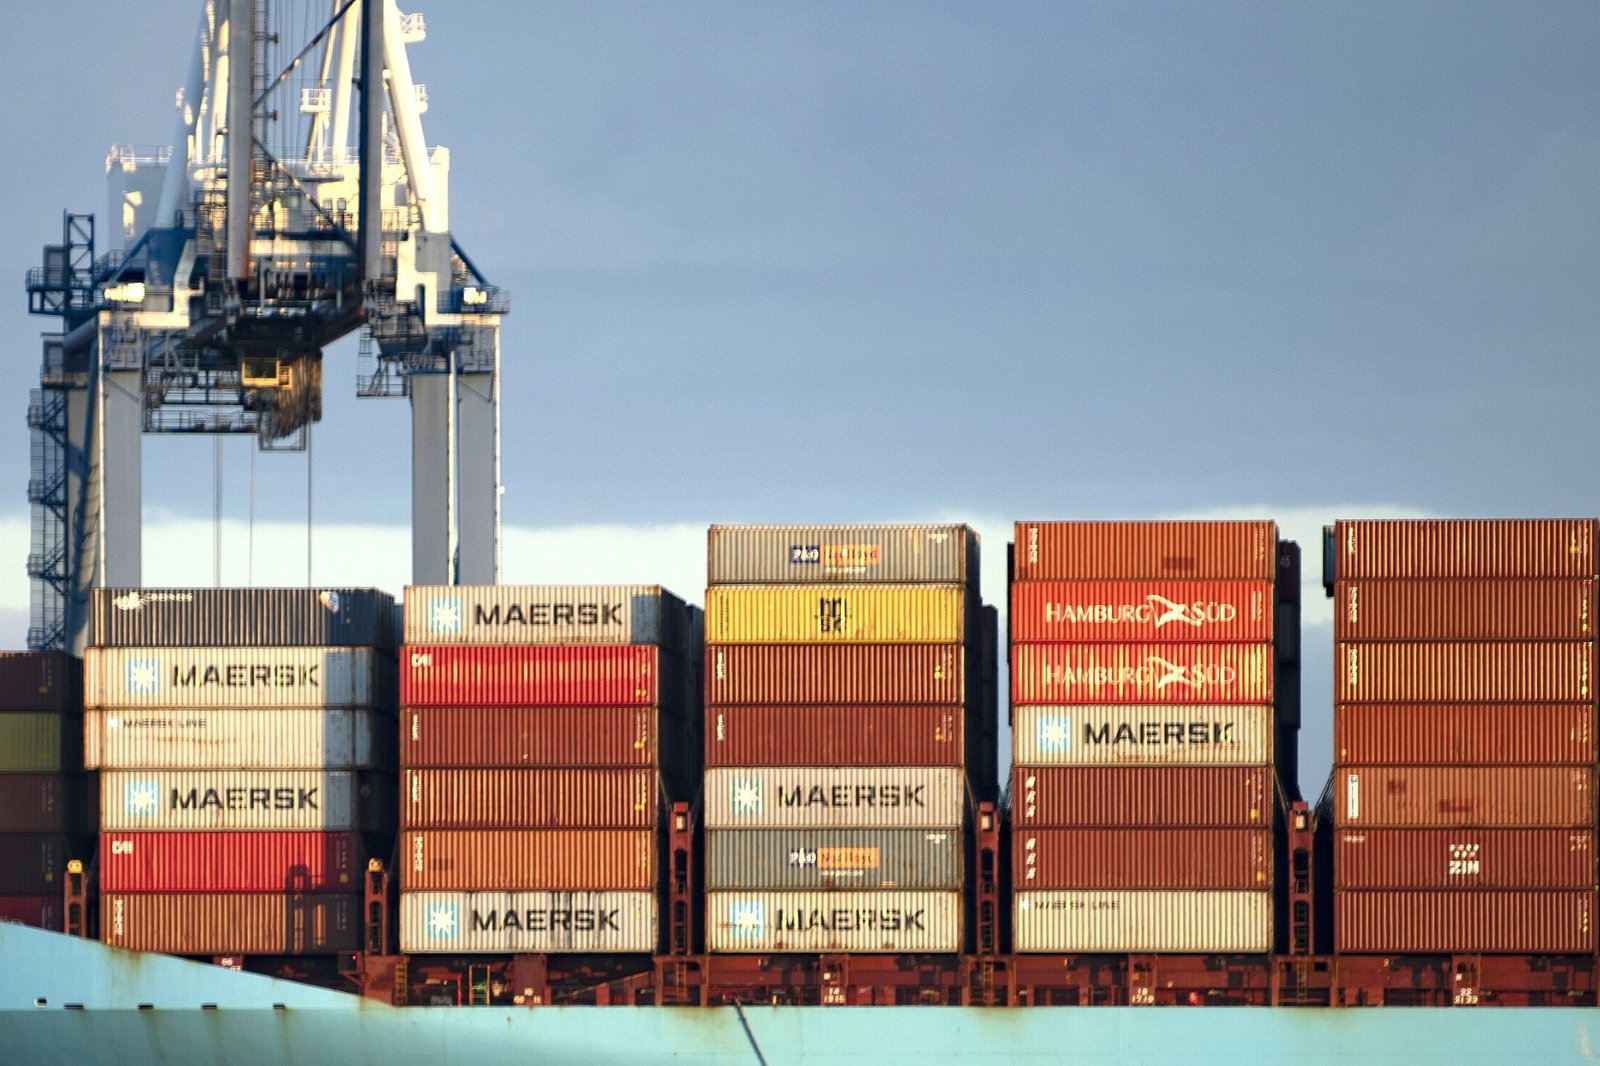
ZPMC is the world’s largest port machinery maker, supplying container cranes and terminal equipment to ports across Asia, Europe and the Americas — a scale that comes from the company’s public footprint, not from any incident reporting. A name this large on a leak site guarantees attention, and attention is precisely what ransom deadlines are built to harvest. Nothing in the reporting suggests operational impact at ZPMC or at any port, and this article will not claim one.
The entry also lands in the China lane, where cyber activity linked to Chinese actors draws the closest monitoring. That lane context is real but separate: our coverage of Artex AI traced a Chinese-linked cyber tool tied to bank heists — a different ecosystem from n0n, which SOCRadar assesses as likely Russia-based. The connection is only this: when a China-based critical-equipment supplier appears on any extortion list, security teams watch the cluster closely, and so should readers.
What the Leak Site Claims About ZPMC’s Data
The entry, as mirrored by the Ervik ransomware victim tracker and the Pulse tracker, reads: “Port machinery / engineering · China | Operational EDI archives and cargo loading records | [NOT PAID — EXPOSED: files publish 2026-10-19 13:27 UTC]”. Ervik prints the caveat in plain words — the disclosure reflects what n0n has publicly claimed on its own leak site, the attacker’s own claim, not independent third-party confirmation. The “NOT PAID” status is the group’s own ledger entry, not proof of any payment or negotiation.
EDI deserves a plain definition, because most readers have shipped through it unknowingly. Electronic data interchange is the machine-to-machine paperwork of cargo: manifests, loading orders, customs messages, and gate instructions that flow between shipping lines, terminal operators, customs brokers and truckers. A port crane operator like ZPMC sits near that paperwork’s operational spine — which is why its claimed EDI archives and cargo loading records would matter if they exist and leak.
Why would extortionists want operational data instead of customer records? Because cargo flow data is quietly sensitive. Volumes reveal business health; partner lists reveal commercial relationships; schedules and routing reveal how a terminal physically runs. None of it is a password database, and none of it is confirmed stolen here — but an extortion price is built on fear of exposure, and operational exposure scares the right people. QPulse’s incident note on the ZPMC listing adds one more discipline point: no technical vulnerability or attack method has been disclosed, and the source does not confirm how entry would have happened.
How to Read a ZPMC Ransom Headline: Claim vs Confirmation
This is the paragraph that matters most. As of October 13–14 reporting, none of the 38 listed maritime organizations had publicly confirmed a breach, and ZPMC had made no public statement our sources could verify. Every sentence describing “stolen” data — including the data attributed to ZPMC — originates from the attacker’s own leak-site post. A ransom deadline is a pressure tool, not a fact. A deadline passing without a leak would not prove innocence, and an actual leak would be the first substantive test of what n0n really holds.
We apply the same claim-versus-confirmation discipline across our security coverage — see our AI data privacy ledger for the same method applied to what platforms hold versus what they admit. The reader habit to build: when you see a company name next to the word “ransom”, ask who is speaking. If it is the attacker’s site, you are reading a claim with a countdown attached — useful as a warning, worthless as a verdict.
What Ports, Cargo Handlers and Suppliers Should Do Now
SOCRadar’s advice targets any organization that exchanges EDI with the named companies — listed or not. Rewritten as plain numbered steps:
- Map your shared systems. List the port community systems, EDI hubs, terminal-system vendors and file-transfer services that carry your cargo data, and ask each provider directly whether it is investigating.
- Patch exposed interfaces first. Check internet-facing EDI, file-transfer and terminal components for missing security updates — our Rapid7 patching report explains why waiting for routine patch cycles is now the wrong cadence for exposed systems.
- Hunt the anomalies. Investigate unusual access or bulk downloads on those shared systems — bulk exports are the fingerprint of data collection.
- Rotate integration credentials. Cycle API keys, EDI mailbox passwords and file-transfer accounts, and check employee and supplier credentials for compromise — our vault login guide covers the storage half of credential hygiene.
- Enforce MFA on remote access. Multi-factor authentication on every remote route into terminal and EDI systems.
- Remove internet-exposed RDP. Remote desktop services reachable from the open internet are an invitation; close them.
- Prepare the communications plan. Draft what you would tell customers and regulators if a third-party provider’s data incident exposes your cargo flows.
- Monitor the group. Watch n0n’s leak-site activity through and past the October 19 deadline for new postings.
The Philippine frame is practical, not decorative: terminals in Manila, Cebu, Subic and Batangas, and the cargo handlers around them, run on the same class of EDI and community systems as the named operators. Per SOCRadar’s guidance, the trigger is a data relationship, not a location — if your systems exchange electronic cargo data with ZPMC or any of the 38, run this checklist this week.
What to Watch After October 19
Three checks turn the deadline into a decision tool. First, does data actually publish at 13:27 UTC on October 19 — and does the volume match the claimed megabyte figures? Second, does any listed organization issue a first confirmation, which would convert a claim into an incident with legal weight? Third, do other extortion groups copy the single-batch, uniform-deadline format, which would signal the tactic works? Add the shared-platform question: whether published samples hint at one common source feeding several victims.
If ZPMC’s files never appear while others publish, that pattern reads as selective pressure, not exoneration — the deadline mechanism was always the point. We will keep this story’s ledger open past the deadline. WorldNgayon delivers Digital Intelligence for the AI-powered world — and the practical next step stays the checklist above, run before the countdown ends rather than after.
Frequently Asked Questions
Has ZPMC confirmed a ransomware attack?
No. As of the October 13–14, 2026 reporting, none of the 38 listed organizations — ZPMC among them — had publicly confirmed a breach. The attack claim exists only on n0n’s leak site, which is the attacker’s own statement.
What data does n0n claim to hold from ZPMC?
The leak-site entry claims operational EDI archives and cargo loading records — the electronic paperwork of cargo operations. That description is unverified and mirrors what the attacker chose to advertise.
What is EDI in shipping, in plain words?
EDI (electronic data interchange) is the automated exchange of cargo paperwork — manifests, loading orders, customs messages and gate instructions — between shipping lines, terminals, customs brokers and truckers. It is how a container moves without a single paper form changing hands.
When would n0n publish the claimed data?
The group set October 19, 2026, 13:27 UTC as the publish time for the whole batch. Treat it as a pressure deadline: it can pass without publication, and publication would be the first real test of what the group actually holds.
Should Philippine ports and logistics firms act?
Any firm exchanging EDI data with a named company should run the eight-step checklist above — map shared systems, ask providers, patch exposed interfaces, rotate credentials — regardless of whether any breach is ever confirmed.
How to Cite This Article
Cite as: WorldNgayon, “Chinese Port Giant ZPMC Caught in a 38-Company Ransom Threat,” October 16, 2026 — worldngayon.com.